
I'm currently using Enpass (www.enpass.io)
are you using that with any kind of two-factor authentication?
Edit// I took the liberty of changing the thread title to "LastPass alternatives with two-factor authentication? (including premium LP)"


 Topic: LastPass alternatives with two-factor authentication? (including premium LP) (Read 68,390 times)


I'm currently using Enpass (www.enpass.io)
I wrote to LastPass support about this and they said it was for their stupid LastPass browser that is also built into the app. I told them the browser was superfluous and that they should separate it into another app if they wanted to include that functionality, because all I wanted from them was to be able to store and retrieve my passwords. They didn't really respond to that.Isn't the problem that Google won't allow extensions to be added to any Android browser by a third party, so the only way to make logins seamless is for the password program's authors make their own browser with the functionality built in? At least, that's what I thought from reading Sticky Password's information.
Every so often, the browser extension's auto-form-fill functionality stops working on sites where it has worked for months (or years). The only way I've found to get it to start working again is to delete the "site" and create it again.I have a vaguely similar problem. I usually use Sticky Password's floating window. Occasionally it won't work with Opera for Android. This appears to be Opera's problem, not SP's, as I also run Clipper+ and find that SP has sent the relevant information to the clipboard. In other words, Opera temporarily won't accept a paste. Rebooting doesn't always clear the problem. However, I also have UC Browser HD as well as Sticky Password's own Sticky Browser, so one or other should work (I hope).
Is there anything out there that provides the convenience of LastPass (secure cloud storage/retrieval) for Android without any of the extra crap?You'd probably feel SP has too much fluff and horsefeathers as well
 But you don't have to actually use all of it.


I wrote to LastPass support about this and they said it was for their stupid LastPass browser that is also built into the app. I told them the browser was superfluous and that they should separate it into another app if they wanted to include that functionality, because all I wanted from them was to be able to store and retrieve my passwords. They didn't really respond to that.Isn't the problem that Google won't allow extensions to be added to any Android browser by a third party, so the only way to make logins seamless is for the password program's authors make their own browser with the functionality built in? At least, that's what I thought from reading Sticky Password's information.

I'm currently using Enpass (www.enpass.io)
are you using that with any kind of two-factor authentication?
Edit// I took the liberty of changing the thread title to "LastPass alternatives with two-factor authentication? (including premium LP)"

Am I the only person in the world who just remembers all of his passwords, instead of trusting any service (be it online or offline) to store it?
Yes.


I'm currently using Enpass (www.enpass.io)


I'm currently using Enpass (www.enpass.io)
I haven't tried it (was a bit surprised by having to enter an email and a captcha for a free download), but a quick google suggests it is a password database that does not offer auto-fill like LastPass and others, is this still the case?
Thanks Deo, for that information. Without a browser extension, I won't be trying it. I use mine a lot to have my passwords available to my wife, and she's not really technical.
Thanks Deo, for that information. Without a browser extension, I won't be trying it. I use mine a lot to have my passwords available to my wife, and she's not really technical.
It can import from LastPass. So you can continue to use LastPass in your browser on your desktop, and just use Enpass on your mobile device, if you'd like.
LastPass is $12/year on mobile. Enpass is a one-time $10 purchase.
well,I'm currently using Enpass (www.enpass.io)
are you using that with any kind of two-factor authentication?
Edit// I took the liberty of changing the thread title to "LastPass alternatives with two-factor authentication? (including premium LP)"
No. But as no user data is stored on their server (which is only used to sync between devices) would it be all that necessary? The data is encrypted by your device and remains on your device(s) so I don't see where some man-in-the-middle attempt would make any difference. All data is encrypyed and local. You wouldn't even need to decrypt in order to synchronize. It would be a little more work for the local clients - but EnPass wouldn't need to worry or know about any of the the actual data.
Am I missing something?
as you know, I'm no expert. But the idea that all anyone needs is one password and then they have access *all* my passwords, and more - I find that pretty scary.
 ) Which is why I memorize passwords to critical things such as my bank accounts etc.
I'm currently using Enpass (www.enpass.io)
I haven't tried it (was a bit surprised by having to enter an email and a captcha for a free download), but a quick google suggests it is a password database that does not offer auto-fill like LastPass and others, is this still the case?
Unfortunately, nobody is quite sure what to replace passwords with. So passwords it is for now.
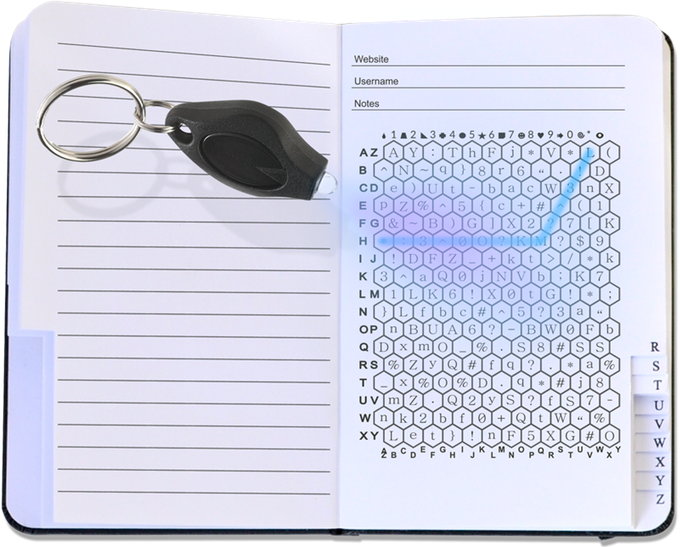
Enigmaze is a Premium Hardcover Notebook Specifically Designed to Quickly Create and Store Strong Passwords.

Isn't the problem that Google won't allow extensions to be added to any Android browser by a third party, so the only way to make logins seamless is for the password program's authors make their own browser with the functionality built in? At least, that's what I thought from reading Sticky Password's information.Perhaps I've misunderstood you, but I thought I should mention that I use LastPass on both the PaleMoon browser for Android and the Dolphin browser for Android. Dolphin has a LastPass for Dolphin extension. I'm not sure what PaleMoon does, but I know LP has worked on the Android version of the browser.

I'm actually starting to use Enigmaze.
So basically, it's time to go back to using PasswordCard?
I'm actually starting to use Enigmaze.
So basically, it's time to go back to using PasswordCard?
Isn't the problem that Google won't allow extensions to be added to any Android browser by a third party [...]Perhaps I've misunderstood you, but I thought I should mention that I use LastPass on both the PaleMoon browser for Android and the Dolphin browser for Android. Dolphin has a LastPass for Dolphin extension.
I don't get how you use that for multiple sites? And you just have to remember where the password is? I like the Enigmaze idea better with a diary and UV light and you can trace any path, though that is an interesting idea I'd not seen.


Security experts constantly tell users not to reuse passwords on multiple accounts, but the message often falls on deaf ears. Now, officials at Mozilla are finding that advanced users don’t always follow that advice either after discovering that an attacker was able to compromise a Bugzilla user’s account by using a password taken from a data breach on a separate site.
I don't get how you use that for multiple sites? And you just have to remember where the password is? I like the Enigmaze idea better with a diary and UV light and you can trace any path, though that is an interesting idea I'd not seen.
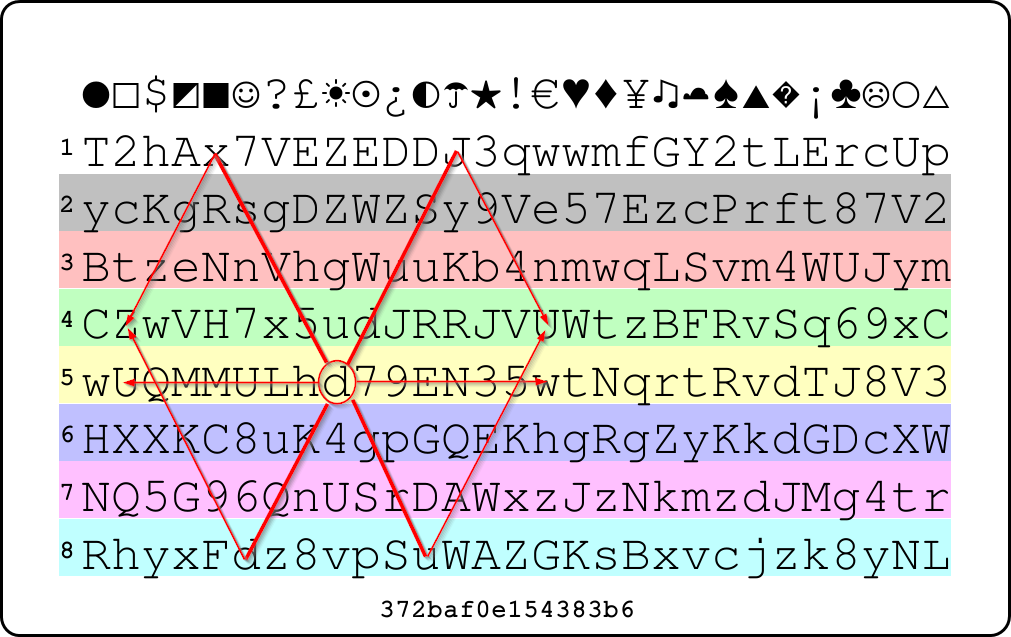
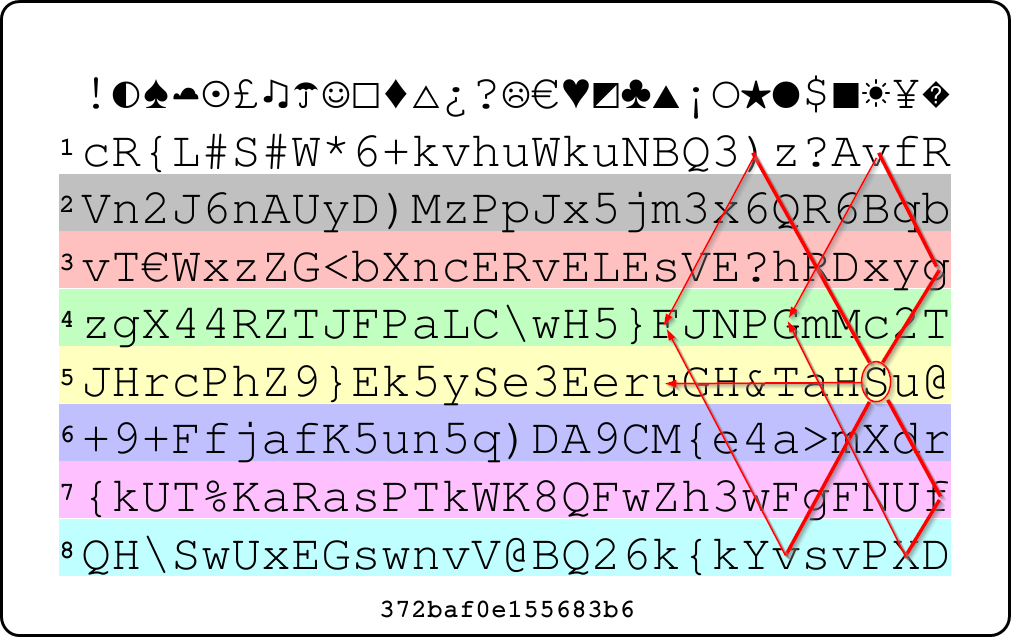
Not sure whether you were referring to how I use them or not but as an example here's two cards, (like I said, I use eight):
[attachment 1 not found] [attachment 2 not found]
Say I choose for my reference Yellow + Sun, without getting too fancy, that gives me six 8+ character passwords on the first, five on the second.
Generally, I'll use the same password, (and an unrelated username to 'normal' sites), across low-grade sites, ie. any site that it doesn't matter if someone logs in as me and screws it up because, quite honestly, I couldn't care less, (I use a throw away Gmail address for these anyway).
For more important sites, (that still don't have direct monetary links, eg. DC), I'll use an individual 8+ character password off one of the cards.
For my VPS' and banks, I use a combination of two of the 8+ character passwords off two of the cards, ie. a 16+ character password, plus TFA.
Shopping sites generally get a combination of two passwords.
For my Gmail addresses I mainly use the same password plus TFA except for two that are used for banking, they have a 28 character passphrases plus TFA.
Also, the number of sites I visit is probably depressingly low compared to other net denizens, so after I've used the various passwords a few times, they've generally stuck in my mind.
The normal way you'd use these cards is you'd only have one and for each site you'd choose a symbol/colour combination but I found that harder to memorise since I then have to associate the arbitrary symbol/colour with a website, then remember which direction to read the password.
So, someone has to choose which one, (or two), of the eight cards I'm using, which symbol/colour I might be starting from, which direction I might be going, and how far along that line I might be traveling.
The eight images are encrypted on my phone, stored online (so I can access from elsewhere), and also a printed out version, using PocketMod, that's the same size as a credit card.
Pretty cool! Thanks for sharing!
Original address: https://www.donationcoder.com/forum/index.php?topic=41106.0