


The Weekly Tech News
 | Hi all. Enjoy  As usual, you can find last week's news here. |
1. IE8 Beats Firefox, Chrome, Opera, and Safari in Battery Life
Spoiler (click to show/hide)
http://arstechnica.com/microsoft/news/2009/09/ie8-beats-firefox-chrome-opera-and-safari-in-battery-life.ars
Finally, a browser comparison with IE on top that sounds remotely believable... IE8 apparently tops all the major browsers in battery usage.
Finally, a browser comparison with IE on top that sounds remotely believable... IE8 apparently tops all the major browsers in battery usage.
Quote
When you think about benchmarking a browser, you typically consider speed, as well as CPU and memory usage. What about battery life, though? Laptop sales are outpacing desktop sales after all, so it only makes sense to choose software based on battery life, in addition to other factors and criteria. AnandTech tested a Gateway laptop with an AMD processor, a Gateway laptop with an Intel processor, and the Asus Eee PC netbook to compare battery life while running Internet Explorer 8, Firefox + AdBlock, Chrome 2, Firefox 3.5.2., Opera 9.64, Opera 10.0b3, and Safari 4. The two Gateways were running Windows Vista, while the Eee PC was running Windows XP SP3. Simple webpages were tested, as well as ones with Flash.
2. France Passes Harsh Anti-P2P Three-strikes Law (again)
Spoiler (click to show/hide)
http://arstechnica.com/tech-policy/news/2009/09/france-passes-harsh-anti-p2p-three-strikes-law-again.ars
After the first version of the law was struck down by federal courts, a newly modified version of the french 3-strikes law has been passed by parliament.
After the first version of the law was struck down by federal courts, a newly modified version of the french 3-strikes law has been passed by parliament.
Quote
The French legislature today passed into law a second version of the ultra-controversial HADOPI "three strikes" law that targets illegal Internet file-swappers. The revised proposal does address the concerns of the "Sages" who sit on France's Constitutional Council who objected to the first version of the law, but it does little to mollify critics. Internet disconnections of up to a year can be ordered by a single judge in a "streamlined" proceeding, while Internet users who fail to "secure" their connections can also be punished if other people use those connections to exchange copyrighted material.
The National Assembly passed HADOPI 2 today by a margin of 285-225; the Senate has already passed the legislation.
3. Google Boosts Book Digitization by Capturing ReCAPTCHA
Spoiler (click to show/hide)
http://arstechnica.com/web/news/2009/09/google-boosts-book-digitization-by-capturing-recaptcha.ars
Google has purchased online service reCAPTCHA in the hopes the service might assist them with their book digitizing effort.
Google has purchased online service reCAPTCHA in the hopes the service might assist them with their book digitizing effort.
Quote
This morning, the Official Google Blog announced that the search giant has acquired reCAPTCHA. The company provides a service that combines two things that Google would be very interested in: it verifies that information provided to a server has been entered by a human and, in the process, helps identify difficult-to-decipher text from book digitization projects. As such, it's a natural fit for Google.
The basic premise of the reCAPTCHA service is based on two related computer science problems. Book digitization efforts rely on the ability of optical character recognition (OCR) software to help extract the text from a scanned image of a page. For a variety of reasons—damage to a book, improperly placed pages, unusual fonts, etc.—this process fails at a certain rate, leaving an incomplete digitization.
4. Disloyal Employees Are Not Hackers, Says Court
Spoiler (click to show/hide)
http://arstechnica.com/tech-policy/news/2009/09/disloyal-employees-are-not-hackers-says-court.ars
This court decision sets a precedent for far less harsh sentences for employees who steal data from their place of employment.
This court decision sets a precedent for far less harsh sentences for employees who steal data from their place of employment.
Quote
The "unauthorized access" provision of the Computer Fraud and Abuse Act (CFAA) has turned out to be quite an asset to those looking to prosecute people for all manner of actions involving computers, even though it was originally meant to target hackers. The Ninth Circuit Court of Appeals has ruled, however, that it cannot be used to prosecute someone for being disloyal with company info after quitting—a decision that is being applauded by CFAA critics who want to limit the statute.
The decision came after a company named LVRC Holdings filed a lawsuit against a former employee, Christopher Brekka, his wife, Carolyn Quain, and their independent consulting business. LVRC had accused Brekka of using company computers "without authorization" in order to e-mail himself LVRC client files in order to use that information for his personal business after leaving the company.
5. Google Apps Bug: You've Got (my) Mail
Spoiler (click to show/hide)
http://news.cnet.com/8301-27080_3-10356803-245.html
A Google Apps snafu saw several university students given access each others' email. Still want your stuff in the cloud people?
A Google Apps snafu saw several university students given access each others' email. Still want your stuff in the cloud people?
Quote
As a result of a bug in a Google Apps e-mail migration tool, some students at Brown University found other students' e-mail in their in-box over the weekend as Google was moving their e-mail from Exchange to Gmail, Google confirmed on Friday.
The problem affected a "handful" of organizations that use Google Apps, a spokesman said. He declined to specify how many were affected or how many individual users were affected.
Brown University newspaper the Brown Daily Herald reported that e-mail for 22 students was misdirected starting on Friday, that the university notified Google about it on Saturday, and it was fixed on Tuesday.
6. Microsoft, Cisco Issue Defenses For TCP Denial-Of-Service Attack
Spoiler (click to show/hide)
http://www.darkreading.com/security/perimeter/showArticle.jhtml?articleID=219700358
Microsoft and Cisco have both released patches for the still as-yet only partially disclosed TCP stack resource exhaustion vulnerability.
Microsoft and Cisco have both released patches for the still as-yet only partially disclosed TCP stack resource exhaustion vulnerability.
Quote
A denial-of-service (DoS) attack threat to Transmission Control Protocol (TCP) implementations reported more than a year ago re-emerged yesterday in the form of security updates from Microsoft and Cisco, with the two vendors each issuing protections against the potentially deadly attacks.
Microsoft and Cisco were the first vendors to address the still mostly mysterious flaws in implementations of TCP that were first revealed last fall by researchers from Outpost24. Details of the attack have been kept under wraps for security reasons, but it basically lets an attacker DoS a PC or router using just a few malicious packets, in some cases permanently damaging victim machines.
7. Australia Mulls Botnet Takedown Scheme
Spoiler (click to show/hide)
http://www.theregister.co.uk/2009/09/15/oz_botnet_takedown_scheme/
Honestly, I'm running out of negative euphemisms for the Australian Government, if it's even worthy of that title anymore... Basically, they've decided that the best way of getting zombie PCs offline is to disconnect their owners from the Internet, an act for which ISPs (of course, who else?) would be responsible.
Honestly, I'm running out of negative euphemisms for the Australian Government, if it's even worthy of that title anymore... Basically, they've decided that the best way of getting zombie PCs offline is to disconnect their owners from the Internet, an act for which ISPs (of course, who else?) would be responsible.
Quote
Australia is considering the adopting of a code that would oblige ISPs to contact, and in extreme cases perhaps even disconnect, customers with malware-infested computers.
The voluntary eSecurity Code is designed to put a squeeze on the estimated 100,000 zombies in Australia, each of which might be capable of kicking out 10,000 junk emails a day.
Pilot data sharing schemes in Australia are praised for resulting in the reduction of malware-infected systems. Around 68 ISPs were involved in a 2007 Australian Internet Security Initiative (AISI) programme credited with reports of 10,000 compromises every day. The scheme cost a relatively modest A$4.7 million over four years.
8. Pirate Bay Buyer Faces Setbacks
Spoiler (click to show/hide)
http://news.bbc.co.uk/2/hi/technology/8263471.stm
Torrent site The Pirate Bay is facing significant setbacks in the pursuit of its sale to Global Gaming Factory after a creditor claimed to be owed almost $200,000 by GGF.
Torrent site The Pirate Bay is facing significant setbacks in the pursuit of its sale to Global Gaming Factory after a creditor claimed to be owed almost $200,000 by GGF.
Quote
The document was filed with a Swedish court by a creditor of Global Gaming Factory (GGF), which outlined plans to buy the site in June.
The creditor - Advatar Systems - is claiming more than 1.3m kronor (£116,000) in unpaid debts.
It is the latest in a long series of hold-ups which have stalled the sale.
Trading in GGF's shares were suspended in August after an investigation was launched into financial irregularities.
9. The Incredible, Amazing, Awesome Apple Keynote
Spoiler (click to show/hide)
http://www.collegehumor.com/video:1921290
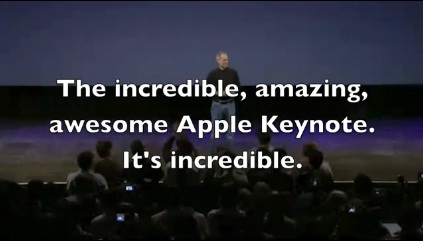
For all of you on the verge of just fragging everyone in a 100 foot radius the next time you hear something about Steve Jobs or apple being so incredible, amazing or awesome, I give you the The Incredible, Amazing, Awesome Apple Keynote.
For all of you on the verge of just fragging everyone in a 100 foot radius the next time you hear something about Steve Jobs or apple being so incredible, amazing or awesome, I give you the The Incredible, Amazing, Awesome Apple Keynote.
Ehtyar.


