DonationCoder.com forum
 
Read-only archive. This is a static copy of the DonationCoder.com forum. Reading and searching work as before; logging in, posting and private messages do not.
Archive of 2026-10-21 · About this archive · Main site

Author Topic: IDEA: LAN Email monitoring  (Read 9,951 times)

wicoralfan

  • Participant
  • Joined in 2006
  • *
  • Posts: 3
IDEA: LAN Email monitoring
« on: April 24, 2006, 02:59 AM »
  Looking for a program to monitor email being written on workstations from one central location. The ability to view both outgoing and incoming messages .
One that does exactly this, is http://www.spytech-web.com/netvizor.shtml
(NetVizor)., however this is very expensive for the amount of licenses I'd need.

Just an idea.

wicoralfan

Gothi[c]

  • DC Server Admin
  • Charter Honorary Member
  • Joined in 2006
  • ***
  • Posts: 873
    • Gathering Badge
    • Coding Snacks
Re: IDEA: LAN Email monitoring
« Reply #1 on: April 24, 2006, 06:48 AM »
You could just use a sniffer that does arp poisening like ettercap ( http://ettercap.sourceforge.net ) or cain ( http://www.oxid.it/cain.html )

wicoralfan

  • Participant
  • Joined in 2006
  • *
  • Posts: 3
Re: IDEA: LAN Email monitoring
« Reply #2 on: June 19, 2006, 04:58 AM »
I'd much rather be able to monitor LAN activities from one central location, or one centrally located machine. Any ideas?

THanks..

Gothi[c]

  • DC Server Admin
  • Charter Honorary Member
  • Joined in 2006
  • ***
  • Posts: 873
    • Gathering Badge
    • Coding Snacks
Re: IDEA: LAN Email monitoring
« Reply #3 on: June 19, 2006, 05:09 AM »
With ARP poisening you CAN monitor from one central location.
It tricks the router in sending all packets through your computer (the one where you want to monitor everything) even if your computer isn't the destination for the packet. This allows you to monitor all lan traffic from one central computer, including email.

wicoralfan

  • Participant
  • Joined in 2006
  • *
  • Posts: 3
Re: IDEA: LAN Email monitoring
« Reply #4 on: June 19, 2006, 05:12 AM »
Thanks for the quick reply. I'll have to look into both of these programs a little further. Which one do you personally recommend?

Thanks again!

Gothi[c]

  • DC Server Admin
  • Charter Honorary Member
  • Joined in 2006
  • ***
  • Posts: 873
    • Gathering Badge
    • Coding Snacks
Re: IDEA: LAN Email monitoring
« Reply #5 on: June 19, 2006, 08:01 AM »
I'd go for ettercap since it can do much more than cain can. Cain is good for sniffing voip stuff.
You can write custom ettercap filters that fetch the email for you.
Ettercap can be fully extended with plugins as well, it requires some scripting from your part, but the tradeoff is that you can completely customise which data to capture and how to process it.

You can use ettercap in combination with ethereal if you want, or any other sniffer. You can use ettercap for arp poisening, and ethereal for filtering data without having to go through any script writing in ettercap.

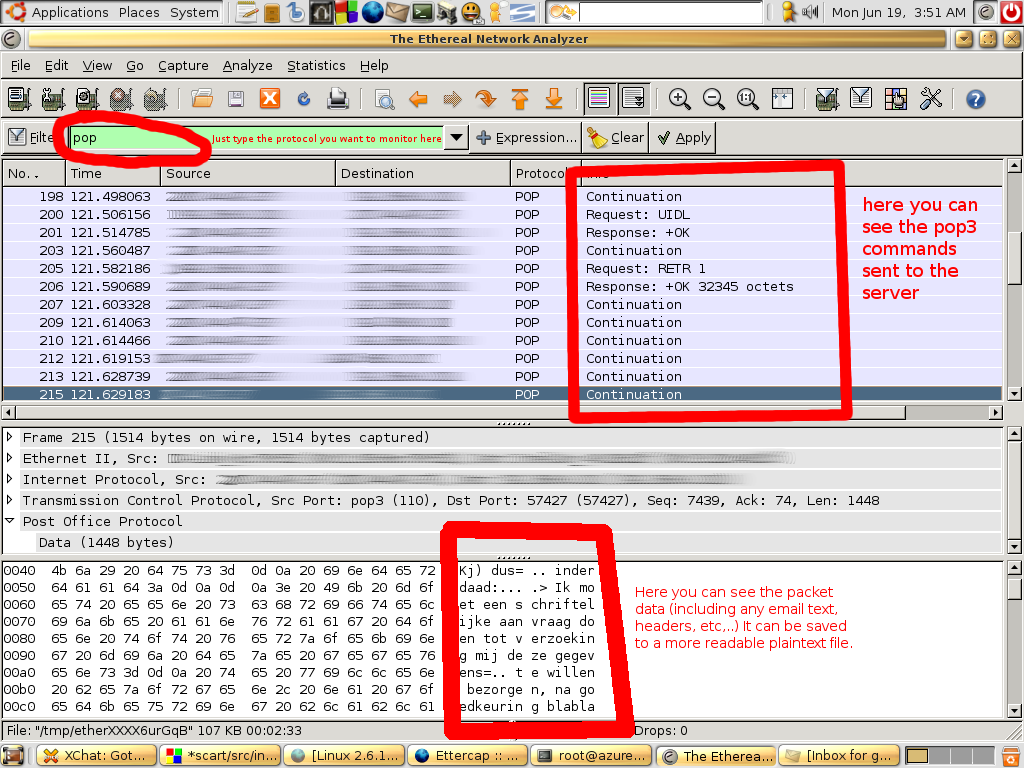
Here is a screenshot with ethereal and an email filter applied. (I only added the pop protocol, you could make it capture both pop and smtp if you want)

Using ettercap's ARP Poisoning features you can capture all data on the network (so not just data from / to your machine)

By default, ethereal captures silently (to avoid overflowing the buffer when allot of data gets sent really fast and there are no filters set.) but you can enable live data monitoring.

(the screenshot is taken on linux but it also runs on windows.)


http://www.ethereal.com/
http://ettercap.sourceforge.net/

« Last Edit: June 19, 2006, 08:07 AM by Gothi[c] »

Gothi[c]

  • DC Server Admin
  • Charter Honorary Member
  • Joined in 2006
  • ***
  • Posts: 873
    • Gathering Badge
    • Coding Snacks
Re: IDEA: LAN Email monitoring
« Reply #6 on: June 19, 2006, 08:28 AM »
by the way, here's the source code for an ettercap filter that will log all email sent over the network to a file, and display a message in the window every time it captures email data. (remember that it needs to be compiled with etterfilter first.)

Code
if (ip.proto == TCP) {
  if (tcp.src == 110 || tcp.src == 25) {
      msg("Captured some email data!");
      log(DATA.data, "C:\\email.log");
  }
}

You can replace the C:\email.log with any file you want to log to, but remember to use double backslashes(\\) because backslash is an escape character in C.


« Last Edit: June 19, 2006, 08:29 AM by Gothi[c] »

Gothi[c]

  • DC Server Admin
  • Charter Honorary Member
  • Joined in 2006
  • ***
  • Posts: 873
    • Gathering Badge
    • Coding Snacks
Re: IDEA: LAN Email monitoring
« Reply #7 on: June 19, 2006, 08:31 AM »
Note that you can also use ethereal with cain, if ettercap looks too difficult. The cain interface is a bit easyer to work with. You can use cain for arp-poisening, and then capture all data in ethereal or any other sniffer.

Original address: https://www.donationcoder.com/forum/index.php?topic=3365.0