


The Weekly Tech News
 | Hi all. Was Black Hat last week y'all, be sure to check out the first story for all the fun stuff  As usual, you can find last week's news here. |
1. BlackHat USA 09 (Links Inside)
Spoiler (click to show/hide)
http://news.cnet.com/Black-Hat-supersizes-in-Las-Vegas/2100-7355_3-6199338.html
Blackhat USA is now over. Get the good stuff. Some of the headline stories:
Using software updates to spread malware (Thanks app)
Security elite pwned on Black Hat eve
Wildcard certificate spoofs web authentication
Text Messages can Hijack your iPhone and Windows Phone
Apple fix to iPhone security flaw
New attack resurrects previously patched security bugs
Hackers: We can bypass San Francisco e-parking meters
Quote
A larger conference means not one but two keynote addresses. One is from Richard Clarke, President Bush's former special adviser on cyberspace security. Clarke, whose 2002 Black Hat keynote speech stated that software vendors and Internet providers must share the blame for malicious software, is now with Good Harbor Security. This year, he will talk about those "who seek truth through science, even when the powerful try to suppress it." The other keynote speaker will be Tony Sager, vulnerability chief of the National Security Agency, who will talk about creating government security standards while working with commercial vendors.
Unlike last year, when Microsoft hosted an entire series of sessions focusing on the yet-to-be released Windows Vista platform, there will be no similar tracks offered this year. Returning tracks include sessions on voice services security, forensics, hardware, zero-day attacks and zero-day defenses. New tracks include operating system kernels, application security, reverse engineering, fuzzing and the testing of application security.
2. BIND Crash Bug Prompts Urgent Update Call
Spoiler (click to show/hide)
http://www.theregister.co.uk/2009/07/29/bind_flaw/
Another oops; a remotely exploitable crash bug has been found in the current version of BIND, triggering the typical mass panic and a swift response from the ISC.
Another oops; a remotely exploitable crash bug has been found in the current version of BIND, triggering the typical mass panic and a swift response from the ISC.
Quote
A vulnerability in BIND creates a means for miscreants to crash vulnerable Domain Name System servers, posing a threat to overall internet stability as a result.
Exploits targeted at BIND (Berkeley Internet Name Domain Server) version 9 are already in circulation, warns the Internet Software Consortium, the group which develops the software. ISC urges sys admins to upgrade immediately, to defend against the "high risk" bug.
Sys admins are urged to upgrade BIND servers to versions 9.4.3-P3, 9.5.1-P3 or 9.6.1-P1 of the software, which defend against the flaw.
3. Microsoft and Yahoo Seal Web Deal
Spoiler (click to show/hide)
http://news.bbc.co.uk/2/hi/business/8174763.stm
Microsoft and Yahoo are teaming up to take on Google. As an end user, I'm sure which is worse, Google or Microsoft + Yahoo...
Microsoft and Yahoo are teaming up to take on Google. As an end user, I'm sure which is worse, Google or Microsoft + Yahoo...
Quote
Microsoft's Bing search engine will power the Yahoo website and Yahoo will in turn become the advertising sales team for Microsoft's online offering.
Yahoo has been struggling to make profits in recent years.
4. UK's National ID Card Unveiled
Spoiler (click to show/hide)
http://news.bbc.co.uk/2/hi/uk_news/politics/8175139.stm
The designs have been unveiled for the UK's national ID card have been unveiled...horay for idiot politicians. AT least they had the sense to make it voluntary, though how long that will last in the practical world is anyone's guess.
The designs have been unveiled for the UK's national ID card have been unveiled...horay for idiot politicians. AT least they had the sense to make it voluntary, though how long that will last in the practical world is anyone's guess.
Quote
The card will be offered to members of the public in the Greater Manchester area from the end of this year.
Ministers plan to launch the £30 biometric ID card nationwide in 2011 or 2012 - but it will not be compulsory.
Opposition spokesmen said it was a "colossal waste of money" and civil liberty groups said it was "as costly to our pockets as to our privacy".
5. US File-sharer Gets $700,000 Fine
Spoiler (click to show/hide)
http://news.bbc.co.uk/2/hi/technology/8177285.stm
And another one bites the dust. At $22,500, this one is slightly less ridiculous than the last...perhaps...
And another one bites the dust. At $22,500, this one is slightly less ridiculous than the last...perhaps...
Quote
The Boston University student, Joel Tenenbaum, had admitted in court that he had downloaded and distributed 30 songs at issue in the case.
It is the second such case to go to trial in the US.
In the first case, a woman in Minneapolis was ordered to pay $1.92m for sharing 24 songs.
On Friday, the jury ordered Mr Tenebaum to pay $22,500 for each infringement. The maximum that he could have been fined was $4.5m.
6. Aussie 'Net Filtering Trial Deemed a Success Despite Problems
Spoiler (click to show/hide)
http://arstechnica.com/tech-policy/news/2009/07/aussie-net-filtering-trial-deemed-a-success-despite-problems.ars
And yet again, Australia shows the world the true prevalence of utter stupidity in this country. I feel so patriotic at the moment...really...
And yet again, Australia shows the world the true prevalence of utter stupidity in this country. I feel so patriotic at the moment...really...
Quote
Although not without controversy, the initial testing of the Australian government's Internet filtering system has gone off fairly well, according to reports from some of the participating ISPs. Five of the nine ISPs testing the government's filtering system reported few problems during testing, even though only 15 customers participated at one and a couple of customers at another were unable to access a completely legal porn site. The other four IPs have either yet to comment on the filter's performance or have refused to talk publicly about the results.
Australia's government first announced its intention to add a Great Barrier Reef of sorts around the nation's virtual shores nearly two years ago, in August 2007. Initial testing began in the island state of Tasmania in February 2008, with cost estimates running as high as AUS$189 million (about US$154 million). The filters were originally intended to be on by default, with consumers able to opt out.
7. Microsoft Blacklists Lenovo's Leaked Windows 7 OEM Key
Spoiler (click to show/hide)
http://arstechnica.com/microsoft/news/2009/07/microsoft-blacklists-lenovos-leaked-windows-7-oem-key.ars
Previous story: http://arstechnica.com/microsoft/news/2009/07/windows-7-ultimate-activation-cracked-with-oem-master-key.ars
Earlier, hackers had found a way to use Lenovo's OEM key to activate pirated copies of Windows 7. Microsoft quickly pulled the thumb out and fixed it.
Previous story: http://arstechnica.com/microsoft/news/2009/07/windows-7-ultimate-activation-cracked-with-oem-master-key.ars
Earlier, hackers had found a way to use Lenovo's OEM key to activate pirated copies of Windows 7. Microsoft quickly pulled the thumb out and fixed it.
Quote
The score was Pirates 1, Microsoft 0, but Redmond has tied it up. Microsoft has blacklisted the Lenovo OEM master key that leaked earlier this week, explaining that "Windows 7 already includes an improved ability to detect hacks, also known as activation exploits, and alert customers who are using a pirated copy" and that "Windows Activation Technologies included in Windows 7 are designed to handle situations such as this one, and customers using these tools and methods should expect Windows to detect them." Microsoft and Lenovo worked together to solve the issue, according to the Genuine Windows Blog:
We've worked with that manufacturer so that customers who purchase genuine copies of Windows 7 from this manufacturer will experience no issues validating their copy of Windows 7. At the same time we will seek to alert customers who are using the leaked key that they are running a non-genuine copy of Windows. It's important to note that no PCs will be sold that will use this key.
8. NASA Hacker Loses Bid to Avoid Extradition
Spoiler (click to show/hide)
http://news.cnet.com/8301-1009_3-10300671-83.html
He still has several avenues of appeal, but Gary McKinnon has lost his fight against extradition in the UK's high court.
He still has several avenues of appeal, but Gary McKinnon has lost his fight against extradition in the UK's high court.
Quote
Gary McKinnon has lost his high court bid in the U.K. to avoid extradition to the U.S. for hacking into military systems.
McKinnon had tried to argue that former home secretary, Jacqui Smith, was legally wrong to push for the extradition despite his diagnosis of Asperger's syndrome and that the director of public prosecutions was also wrong to opt for extradition despite having sufficient evidence to prosecute McKinnon in the U.K.
However, Lord Justice Stanley Burnton and Justice Alan Wilkie dismissed both claims on Friday. McKinnon now has 28 days to launch an appeal at the Royal Courts of Justice. According to his solicitor, Karen Todner, McKinnon and his legal team will also appeal to the Law Lords, and Todner has made a fresh approach to President Obama
9. Dutch Judge Orders Pirate Bay to Block Netherlands Surfers
Spoiler (click to show/hide)
http://arstechnica.com/tech-policy/news/2009/07/dutch-judge-orders-pirate-bay-blocked.ars

Quote
An Amsterdam court has ordered The Pirate Bay to block all Dutch visitors to its website, threatening the site administrators with daily fines for noncompliance.
Dutch antipiracy group Stichting BREIN, whose website is still down from an extended denial of service attack, filed a suit against the three Pirate Bay administrators who were found guilty earlier this year of aiding copyright infringement in Sweden—despite the fact that the three claim not to own the site. (They say it is owned by a Seychelles company called Reservella.)
None of the men showed up in the Dutch court, claiming they had heard nothing of the lawsuit (BREIN says that it contacted them through mail, e-mail, Twitter, and Facebook). Peter Sunde, The Pirate Bay's most public face, also announced that he was filing a defamation suit (in Sweden) against Tim Kuik, BREIN's chief.
10. AT&T: 4chan Block Due to DDoS Attack Coming from 4chan IPs
Spoiler (click to show/hide)
http://arstechnica.com/telecom/news/2009/07/att-4chan-block-due-to-ddos-attack-coming-from-4chan-ips.ars
AT&T made the mistake of protecting their users from an alleged DoS attack, and incurred the wrath of 4chan.
AT&T made the mistake of protecting their users from an alleged DoS attack, and incurred the wrath of 4chan.
Quote
This weekend did not go well for AT&T. The broadband provider began blocking access to parts of 4chan on Sunday (img.4chan.org, which of course includes /b/) thanks to what AT&T says was a denial of service attack coming from that domain. AT&T was uncommunicative with customers at the onset of the 4chan blockage, leaving many users questioning whether the telecom was trying to censor 4chan. AT&T's official silence on the matter also led some 4chan denizens to launch attacks against the company.
The block began in the early evening Sunday and went on through the night, with numerous users (including some of our own staff members) confirming that they were unable to access 4chan's image servers. Why? According to an Anonymous posting on 4chan itself, it seems as if there were hundreds of thousands of connections being made from the IP address of the image server (888,979 at the time of that posting, to be exact).
11. Another New AES Attack
Spoiler (click to show/hide)
http://www.schneier.com/blog/archives/2009/07/another_new_aes.html
This time, it looks as though the implementation with the smallest key length comes out on top, but there's still plenty of time to beef up the algo before things get too scary.
This time, it looks as though the implementation with the smallest key length comes out on top, but there's still plenty of time to beef up the algo before things get too scary.
Quote
A new and very impressive attack against AES has just been announced.
Over the past couple of months, there have been two (the second blogged about here) new cryptanalysis papers on AES. The attacks presented in the paper are not practical -- they're far too complex, they're related-key attacks, and they're against larger-key versions and not the 128-bit version that most implementations use -- but they are impressive pieces of work all the same.
This new attack, by Alex Biryukov, Orr Dunkelman, Nathan Keller, Dmitry Khovratovich, and Adi Shamir, is much more devastating.
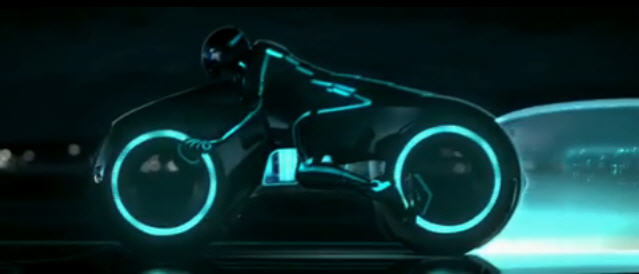
12. Tron Legacy
Spoiler (click to show/hide)
Ehtyar.


