


NANY 2009 Entry Information
| Application Name | Crush Cryptonizer |
| Version | V1.1b |
| Short Description | Scramble short files in an absolute super-secure way |
| Supported OSes | Windows |
| Web Page | - |
| Download Link | Crush Cryptonizer V1.1b |
| Sourcecode | Crush Cryptonizer V1.1b Sourcecode |
| System Requirements |
|
| Version History |
|
| Author | Crush |

Description
You can crypt/decrypt in an extremely high secure way short files. I´d say there´s currently no harder encryption existing. It´s not based on standard crypting routines like AES, Serpent or Twofish and hashes like RipeMD, SHA or others. The program has exclusive in-built cruelty-cryptonite that makes it unusable for realtime-encryption/decryption!
Features
The strength is its combination of iteration calculations, salt generation, code-shuffle algorithm that gives you the power to decide how long someone will take to decrypt it properly. This means: You can crypt a 4-byte text as example so hard that the decryption with the key could take several years on a Cray XT5 supercomputer if you like
 - the only problem is: You also need the same time to encrypt

Technical information:
A number, password or file can be used as input salt. Even if you take the same settings for encryption your encrypted file will be everytime totally different. During the whole process a shuffle-index is recalculated constantly from the results and the actual salt/key. The datas are eored and shuffled with the complete salt. Shuffling means the bytes are changed in the destination datas and the salt itself and so change the next following encryption pass. If the salt is longer than the datas to encrypt it starts at the beginning with this predure - so the start position of the encryption can change every loop. While shuffling it calculates from the actual salt a new shuffle-index in a ping-pong way. This index shuffles the salt itself. It´s because of the nature of the calculation impossible to shorten the encryption in any way. You need to calculate the whole way back with all iterations to get to the original datas and to decrypt all you also need the position where to start in the salt. It´s not even the most imaginable secure way to crypt datas. Additionally it fully supports One-time pads. That is till now with right usage an uncrackable way of encryption (Wikipedia cit.: "The one-time-pad is the only cryptosystem with perfect secrecy... OTP can be used, along with a more standard cryptosystem, in a superencryption scheme).
Planned Features
Usage
Installation
You need nothing special to do - only run the .exe file
Using the Application
Read the readme.txt
Uninstallation
Only delete the file
Known Issues
none at the moment
Screenshot
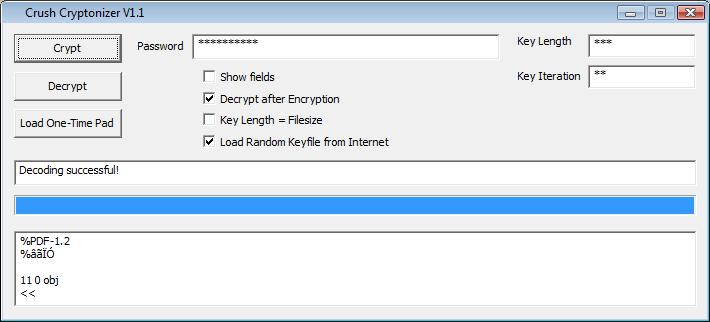
 The Keylength will be set to the Filesize that will be scrambled. Load One-Time-Pad selects a complete File as a Password. This will later set the "Set Key to Filesize" hook active. Crypt let you select the file and starts without waiting. The Crypted file will be saved after encryption and the name gets ended by .cCrypt. Decrypt makes the same to the other direction (deletes the .cCrypt at the end and saves the original filename). Please use this version only for testing, because the Randomizer, CRC and Encryption-Algorithm will be changed by others for the release. If the Decryption not successful the file will not be saved.


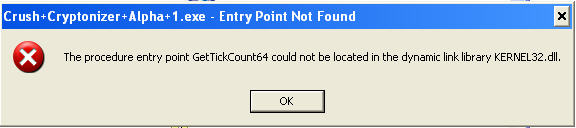
 I haven´t remarked this function is Vista-only. Please try the new file.


 - carpe noctem

 , ok - it´s your decision


 Some very bad news for germans have come up today:


