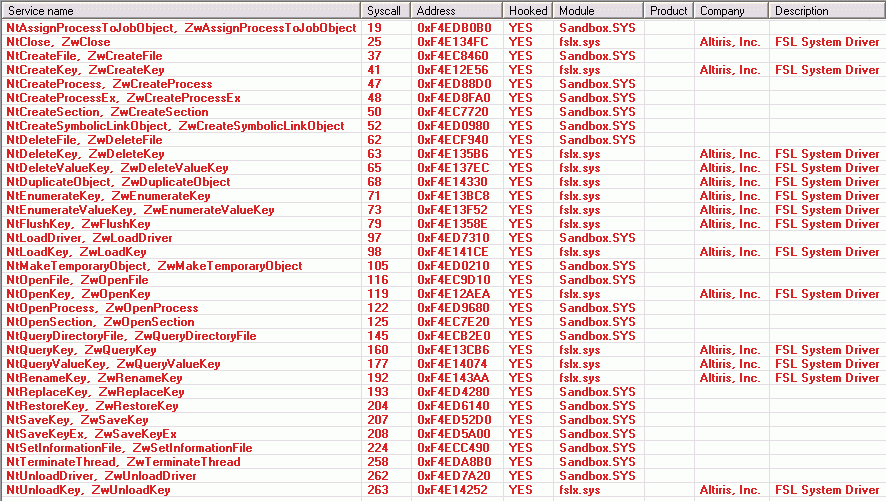
I ran 3 rootkit detectors and got 3 very different results. I could choose to write a long story here about this and tell the details, but in the end the one thing this post really is about, is How on earth dumm users like me are supposed to handle such results? If I (by accident) haven't known any better these scannings would have made me remove several perfectly harmless programs!
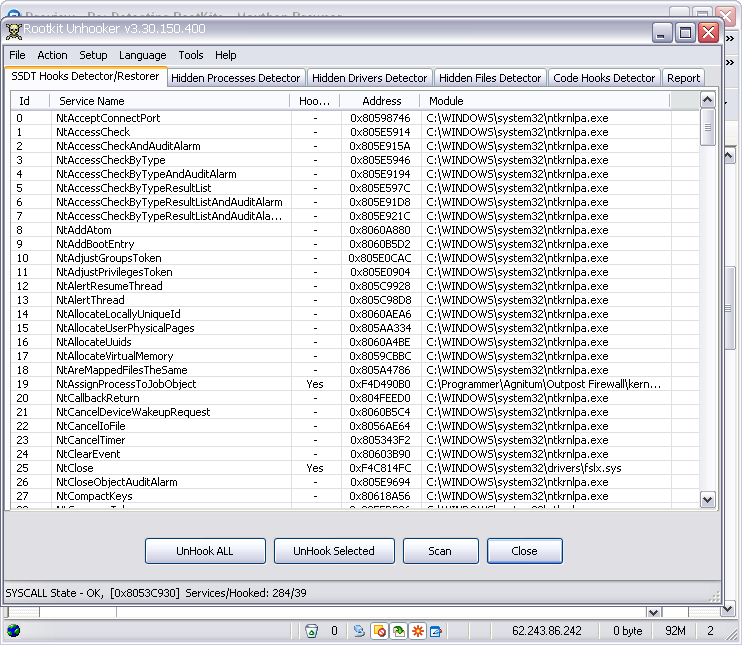
Resplendence RootKit Hook Analyzer 3.00's result:
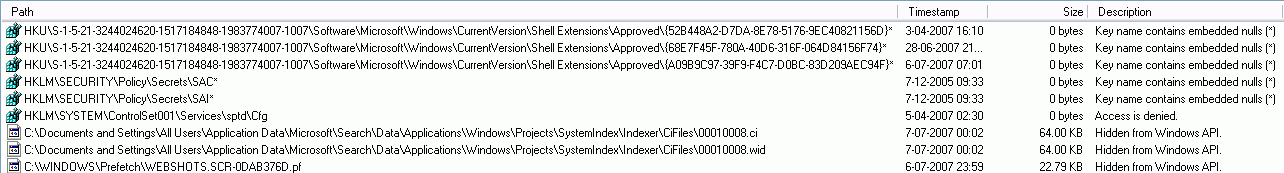
SysInternals RootkitRevealer 1.71 was no better:
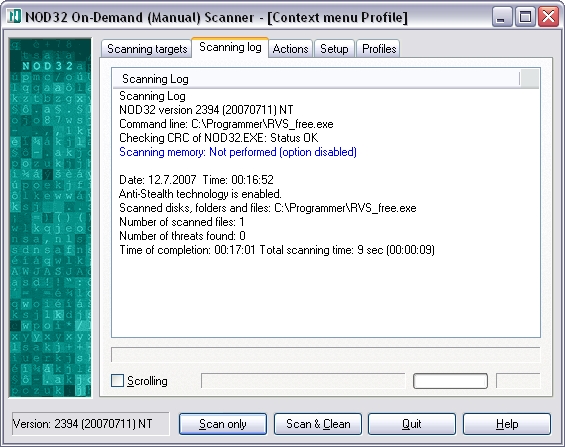
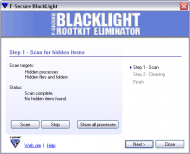
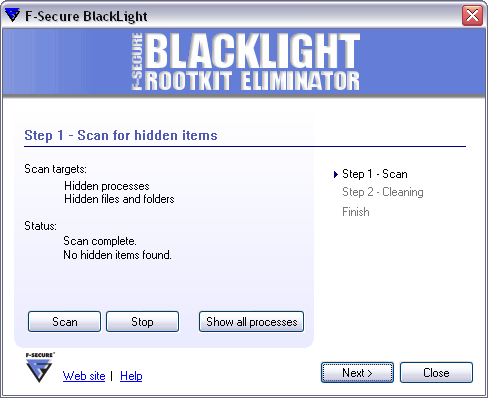
F-Secure Blacklight Rootkit Eliminator (expire 1'st October 2007) gave the only trustworthy result: "0 files found":
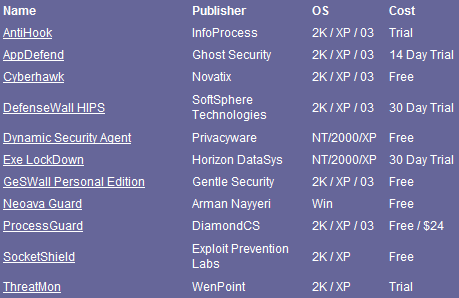
It would be very interesting to see if security tools like Process Guard 3.4 or Anti Hook 3.0 (or the older but free 2.6) would have prevented any of these false-positive-programs from installing! ???
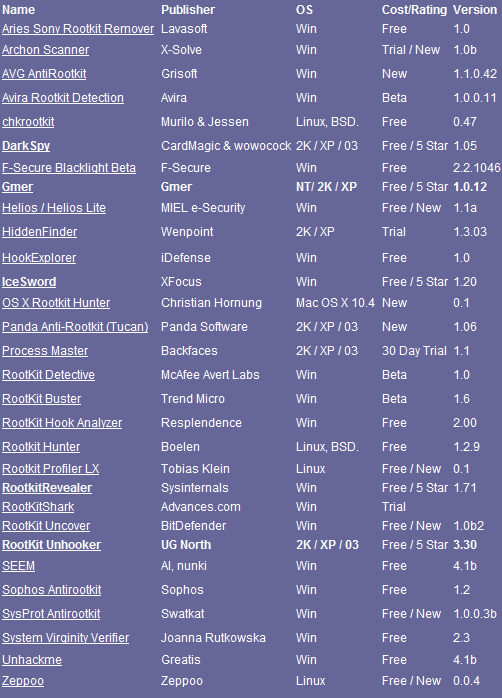
You can read about the rootkit problem at Gizmo's page.
Resplendence RootKit Hook Analyzer 3.00's result:
SysInternals RootkitRevealer 1.71 was no better:
F-Secure Blacklight Rootkit Eliminator (expire 1'st October 2007) gave the only trustworthy result: "0 files found":
It would be very interesting to see if security tools like Process Guard 3.4 or Anti Hook 3.0 (or the older but free 2.6) would have prevented any of these false-positive-programs from installing! ???
You can read about the rootkit problem at Gizmo's page.




 VanDragt.com
 more justice!


 - carpe noctem