
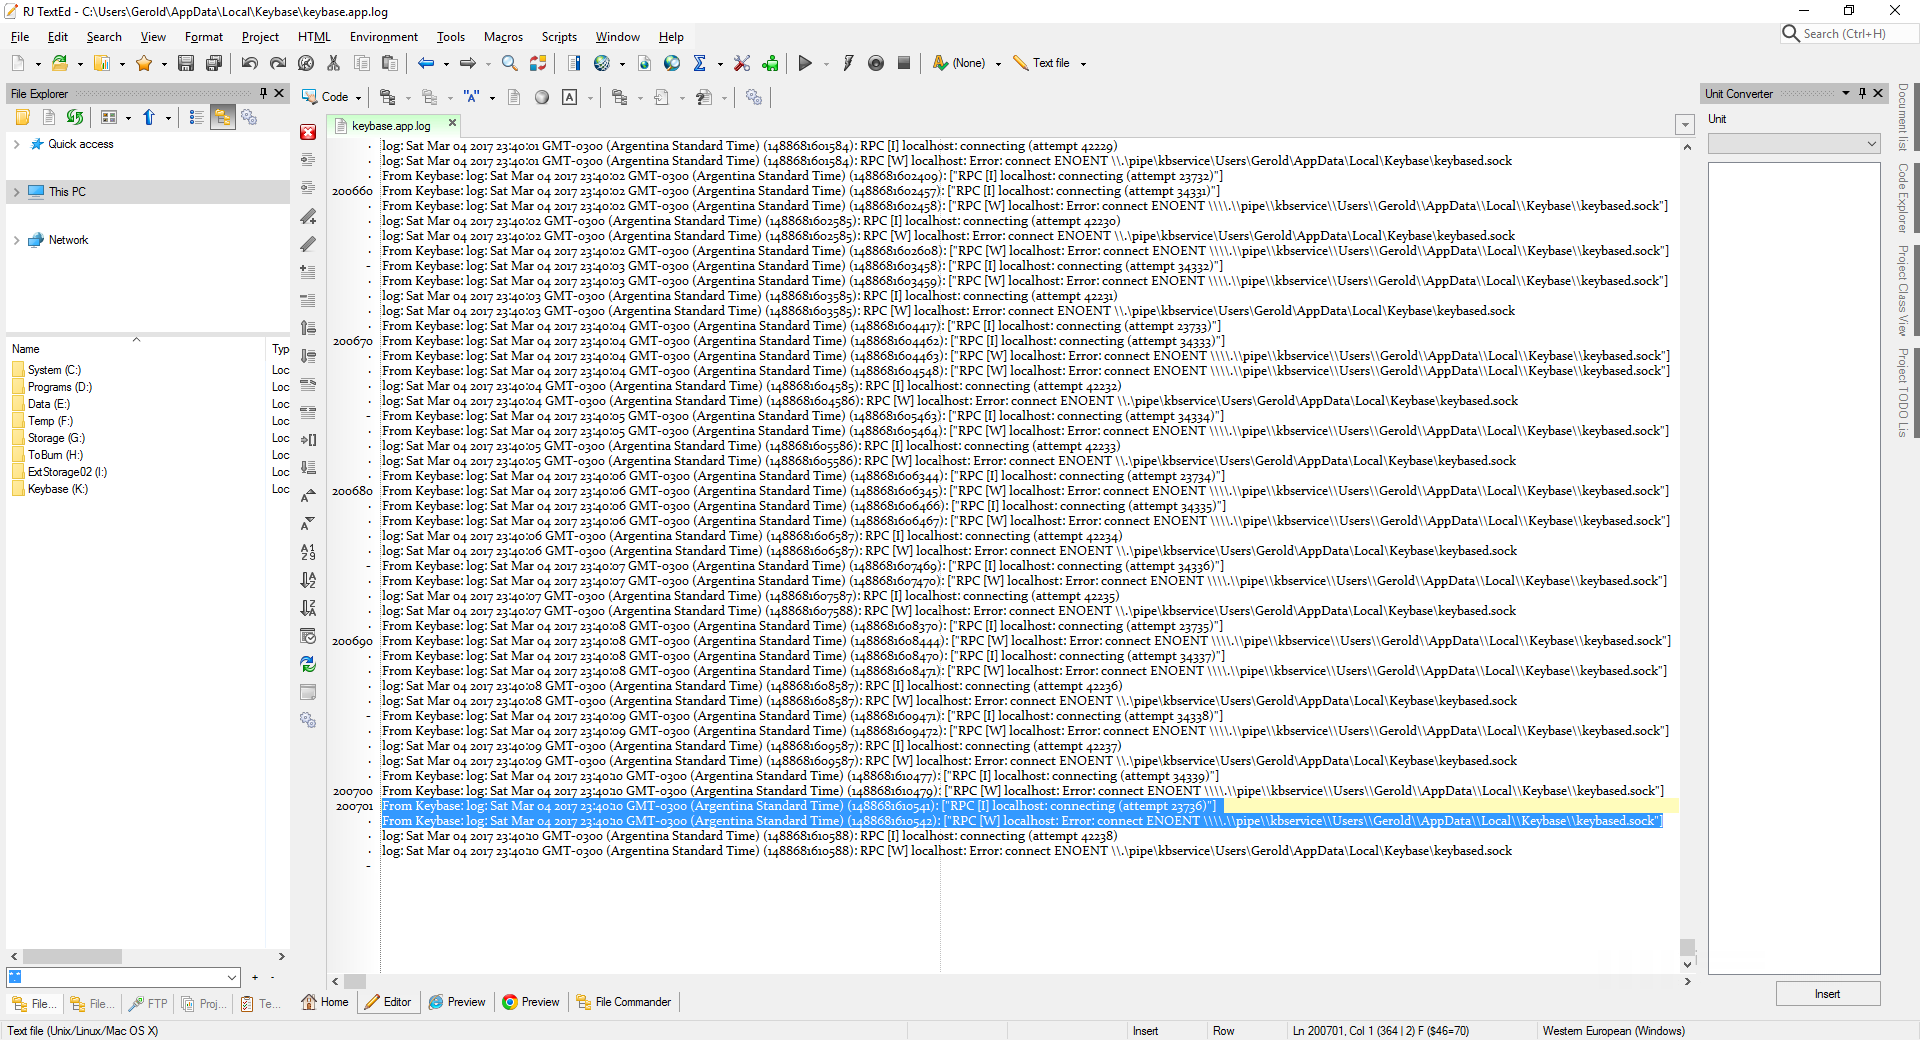
Keybase updated itself today and now I'm stuck on the loading screen again...
Mine did also, but it worked flawlessly. I'm going to try on my other machine, because it didn't autoupdate, and see if I get the same results.


 Topic: Keybase and the Keybase Filesystem (KBFS) (Read 39,449 times)


Keybase updated itself today and now I'm stuck on the loading screen again...


Keybase updated itself today and now I'm stuck on the loading screen again...
Mine did also, but it worked flawlessly. I'm going to try on my other machine, because it didn't autoupdate, and see if I get the same results.

Seriously, use a tool like Revo Uninstaller Pro

I've wondered if maybe there is a connection being blocked by my ad blocker. But according to the Github issue I linked earlier, it seems to be a lack of write access to the directory that is causing the problems.
I've wondered if maybe there is a connection being blocked by my ad blocker. But according to the Github issue I linked earlier, it seems to be a lack of write access to the directory that is causing the problems.Do you know the directory in question?
 ), you can copy and paste it onto https://keybase.io/verify. But if there's some interest from others here let me know and I'll invite you to join. Or you can request access yourself using the command line:
keybase team request-access donationcoderThis is only the beginning; the GUI is evolving fast and we'll have another announcement in ~2 weeks about encrypted git for teams. (Spoiler: truly private repos.)

Ok, now the request does work in the Keybase installation on my Windows computer.


I have installed Keybase. I see Deozaan uses also.
Do you recommend https://ipfs.io/docs/getting-started/ also, or is enough with Keybase ?

It is end-to-end encrypted. It's hosted, like, say, GitHub, but only you (and teammates) can decrypt any of it. To Keybase, all is but a garbled mess. To you, it's a regular checkout with no extra steps.
Even your repository names and branch names are encrypted, and thus unreadable by Keybase staff or infiltrators.
We think this is better than paying a fee to store it in plaintext. Remember, it is impossible to delete cloud data with any kind of confidence, and your host may already be compromised.
Everything is signed.
All data you push is signed by your device's private key, which never leaves your device. Fetches are cryptographically verified or else they'll fail. Unlike casual PGP signing of commits, which no one in the world ever does, this is fully enforced for yourself or team.
You don't need to think about it: if you do a git pull, you'll only get the data if it's bit-for-bit exactly what the pusher pushed.
Looks interesting- but it's not in my installation, which makes me sad.
Original address: https://www.donationcoder.com/forum/index.php?topic=42298.0