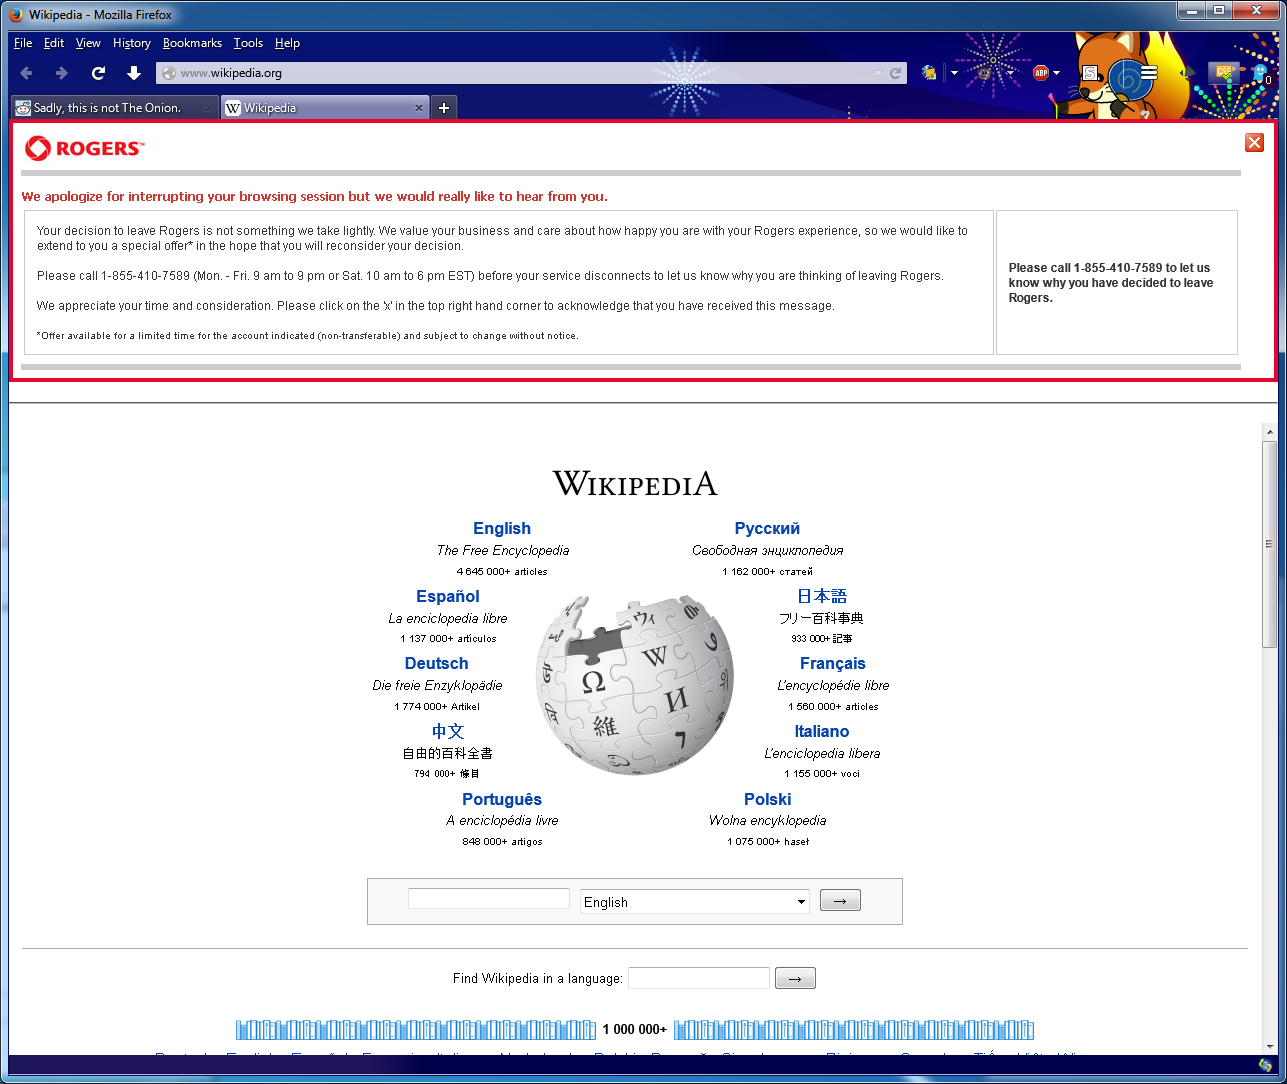
This is rather interesting - an ISP attacking its customers:
http://www.reddit.com/r/canada/comments/2nv1un/rogers_still_using_content_injection_after_7/
[attachthumb=#]
A security video on the topic:
http://2014.video.sector.ca/video/110367213
See 3:31 in the video for another Rogers MITM attack.
The video goes into some good depth on how the ISP is attacking customers.
Here's one good post from the Reddit thread:
Quote
This is borderline criminal. They are modifying the content of a webpage that you are accessing. They are actively injecting their code in a page that you have requesting...
It's beyond a simple gaffe... If they wanted to, they could use this to change what's written in a article from the Globe & Mail or from the CBC...
When they start doing this, there is usually no end...
Now imagine if they decided to change any comment that they find damageable to their brand on twitter or facebook or reddit...
Now imagine they changed the prices on their competitor's website (Bell, Telus) to make them look more expensive than their own...
That's why everyone should always browse the net at the least in HTTPS... Wikipedia article on HTTPS
What you need to know is that HTTPS, when activated, creates an encrypted conduit between you and the webpage you are accessing. It also minimize the amount of information your ISP can intercept when you are browsing the net.
Whenever you do your banking or buying from a reputable site, HTTPS is enabled by default. You can also browse Reddit in HTTPS mode.
Everyone here should be using HTTPS Everywhere from the good people at the Electronic Frontier Foundation. INSTALL IT !