After a number of recent discussions about email privacy and security, I decided to ask this question here and elsewhere, as I am curious as to the responses among DC members and the general public.


I know what it is, but I am not using it.
+1 - Because all encrypted communications do is draw unnecessary attention to your activities, and regardless of what you use it's not going to stop an elite focused (governmental...) attack. So the bulk of it strikes me as a waste of (cycle) time.
I know what it is, but I am not using it.
+1 - Because all encrypted communications do is draw unnecessary attention to your activities, and regardless of what you use it's not going to stop an elite focused (governmental...) attack. So the bulk of it strikes me as a waste of (cycle) time.
I don't think it would be a waste of time if one were a business and it was used for securely transferring password information between you and a client, but in the case of businesses that deal with common people that don't have any clue what PGP or an alternative is, or don't have what they need to use it installed, then it certainly makes things much more difficult to transfer that type of information securely (which is a problem I am facing right now, and to which I have not found a free easy moron-proof cross-platform solution)
I'm in favor of the single use ephemeral "reset" password scheme.What is this?
I've done a variation on that for clients (in a pinch) if I know they are sitting there waiting/trying to login. I log into the server, set their account to require a pw change on next login, and then Email the password to where ever they would like because it ain't gonna be any good in less than 60 seconds anyhow.
I really don't think there is a truly secure way of sending passwords. You can try encrypting it sure...but then what do you do with the encryption key (Infinite loop anybody?)??

I really don't think there is a truly secure way of sending passwords. You can try encrypting it sure...but then what do you do with the encryption key (Infinite loop anybody?)??
Go scuba diving in an underwater cave with a grease pencil and board to write on. Oh, and a good memory as you don't can't do this twice. Erase the board after you're done then set charges and blow up the cave after you leave - NOT before you leave! Important point there - AFTER! Not before!![]()
![]()
Never underestimate the intelligence of dolphins. I am pretty sure they would hack your website, if given the chance...and your password.

My situation is slightly different, in that I need Grandma Dum-Dum to be able to send the info to me, not the other way around. And if after receiving the info, I go and change her passwords on her (because she sent them insecurely), and she can't log into her cpanel or ftp, she is going to panic and think I have hijacked her website instead of securing it for her. I'd like to be able to have her give the info to me securely, use it to complete the job she hired me for, then suggest she change the passwords when the job is done. If at that point she doesn't take my advice, at least with it being me that has the password info, with my knowing I won't do anything harmful with it (if I can't trust myself, then who can I trust?), I won't have to worry as much.
Why can't they create a new user for you? That's what I do in those cases. And if she knows how to use cpanel, then that's not that big of a deal to do. Same for wordpress.
...Dum-Dum...
A polished solution for this should have been part of thunderbird for a decade instead of relying on clunky plugins or obscure tools if it should have had any chance.
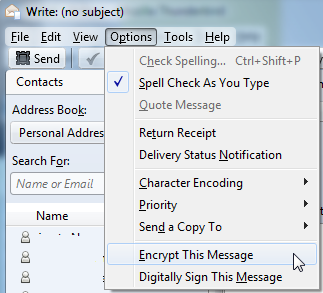
I can't tell you how long it's been there but Thunderbird->Write->Options->Encrypt Message
.Also, almost no one I write to uses it or wants to be bothered.
The other side of the problem is the solution providers. As someone has already noted, self signed security like PGP can be hard to trust but third party providers are inherently risky as well. Even if they're trustworthy, they represent single points of vulnerability which can impact everybody everywhere. A web of trust is the only solution to both problems but it needs to involve the industry players as well.
There are a couple big problems the way I see it, and they're not specific to email. The first is simplicity and useability. For ordinary people something like PGP is obviously way too complicated - not because it's actually that hard but because it has the appearance of difficulty. Honestly, though, even something relatively simple like just going to Comodo and getting a free SSL certificate is just as intimidating.

The other side of the problem is the solution providers. As someone has already noted, self signed security like PGP can be hard to trust but third party providers are inherently risky as well. Even if they're trustworthy, they represent single points of vulnerability which can impact everybody everywhere. A web of trust is the only solution to both problems but it needs to involve the industry players as well.
And that's EXACTLY why I'm hopeful for Bitmessage to sort its problems and enter the arena of strong encryption that we can trust.
Services like that are also important because if/when they become successful there's another piece of the roadmap for developing other services.This is the biggest problem right now.
While I *could* get it working for *ME*... doesn't mean jack if other people aren't on board.
The barrier is a function of difficulty, tech savviness, broad adoption, and willingness to use it. And willingness is a function of "how damn long will this take me to get it running, and who can I use it with?" Blah blah, etc. etc.
I've had a bitch of a time trying to get other people to use Jitsi with me. So far I've got 1 (one) friend to use Jitsi with me. And half the time we end up on Skype. Jitsi is great, but it ain't prime time yet.![]()
Then there's email... hopeless. It's just total dog s4!+.
Original address: https://www.donationcoder.com/forum/index.php?topic=35805.0