


Source: http://thepileof.blogspot.com/2012/03/apaches-server-status-vfolder.html ; (one of my misc blogs)
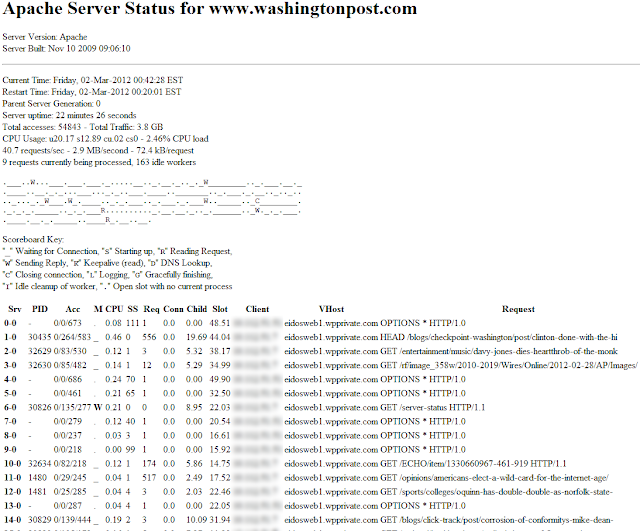
I describe this all on my blog. Basically, the default Apache configuration includes mod_status (a 'base' module, meaning statically linked by default), and many server admins don't bother securing it. This means all client IPs, and their server requests, are being revealed in real time to anyone who wants it.
The concerns are for cases where:
1. There is sensitive info on the query string
2. Security through obfuscation - uniquely named files and folders
3. Privacy concerns since these stats can be polled/refreshed and a pretty good database of activity from the server can be formed.
Apache sets a bad example, with both Apache.org and PHP.NET both being wide open. hXXp://php(dot)net/server-status or hXXp://apache(dot)org/server-status . Wired is even open, at least some of its servers. It depends on which one you hit since they are load balanced. It seems about half of them are 'open', the other half properly secured.


