Has anyone tried (I have and it works) using mail2web ... ? It looks really useful BUT would you give your email password to someone you don't know ?
Would you trust this ... ?
« on: September 15, 2011, 10:36 AM »

 Topic: Would you trust this ... ? (Read 23,882 times)


...BUT would you give your email password to someone you don't know ?


It just seems weird to stick your password into some strange input box.


How this service is any different from thunderbirdIn terms of security it poses a much larger risk, I think.
or any similar thunderbird like web interface software ?I believe any web-based solution would suffer from the problem I mentioned above, and for me it would be the same situation as this. Like Renegade said,
...BUT would you give your email password to someone you don't know ?No. Never.


Gmail can do this too, right? Or are their target consumers not supposed to know about web mail? I think you can even send from the non-Gmail SMTP address.

Ahem... On the "let's give people the keys to the castle" note...
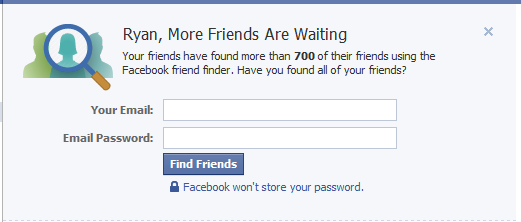
Seems like Facebook is asking for my email address and password...
Ahem... To make this a fun game of fill in the blanks, they can:
G_ f___ themselves.
Like really? WTF? Are they on crack?
Ahem... On the "let's give people the keys to the castle" note...
Seems like Facebook is asking for my email address and password...
(see attachment in previous post)
Ahem... To make this a fun game of fill in the blanks, they can:
G_ f___ themselves.
Like really? WTF? Are they on crack?


I was under the impression that passwords for e-mail were sent in plain text anyway. Has SSL changed that?An SSL connection is encrypted by default, so even though the password goes into the comms channel in plain text, because of the entire channel being encrypted, nobody but the receiving end can read it. It's just like with https vs http websites.

An SSL connection is encrypted by default, so even though the password goes into the comms channel in plain text, because of the entire channel being encrypted, nobody but the receiving end can read it. It's just like with https vs http websites....unless there's a man-in-the-middle with a forged certificate... used to be "zomg tinfoilhat!" stuff, until the latest CA hacks (diginotar, anyone?). Also, HTTPS == HTTP-over-SSL.
 - carpe noctem
@Ath: Thanks! I suspect 4wd's comment about mail2web pre-dating Gmail and other Web mail interfaces probably means it also pre-dates SSL, though they should now catch up and add it.
Well, well... sounds like one more reason to trust mail2web after all@Ath: Thanks! I suspect 4wd's comment about mail2web pre-dating Gmail and other Web mail interfaces probably means it also pre-dates SSL, though they should now catch up and add it.
Already there, just use https://www.mail2web.com - if you can believe Wikipedia, HTTPS was created in 1994, (3 years before mail2web), by Netscape but not formerly specified until 2000.

Original address: https://www.donationcoder.com/forum/index.php?topic=28021.0