DonationCoder.com forum
 
Read-only archive. This is a static copy of the DonationCoder.com forum. Reading and searching work as before; logging in, posting and private messages do not.
Archive of 2026-10-21 · About this archive · Main site

Author Topic: NANY 2009 Release: PESplash  (Read 29,815 times)

seedling

  • Charter Member
  • Joined in 2005
  • ***
  • Posts: 129
    • Participated in NANY Challenge Twice
    • Coding Snacks
NANY 2009 Release: PESplash
« on: December 26, 2008, 04:08 AM »
NANY 2009 Entry Information

Application Name PESplash
Version v1.7.0.11
Short Description this tool will attempt to embed text information into a CODE section of
any PE file. it does so by finding valid opcode strings and replaces
them with "like-minded" opcodes therefore not changing the size or
operability of the file.
Supported OSes Windows 32-bit
Web Page http://seedling.dcmembers.com
Download Link http://seedling.dcmembers.com/other/PESplash.zip
not much, just Win32 OS
v1.7.0.11
  • v1.7.10
    -------
    fixed a bug that would randomly corrupt text in both embedding and
    retrieving process

    improved the retrieving routine and can now get watermark text
    much faster!

    v1.7
    ----
    inserts a default 'save as' filename once the 'open' file is
    selected.
    --------------------------------------------------------------
    this could possibly cause problems since the routine
    uses the '.' as a deliminator and renames the file. an example
    of a problem would be in a path with '.' used in the name:

    C:\stuff.i.like.a.lot\file.exe

    would result in:

    C:\stuffw.i

    since, by default, it simply adds a 'w' after the filename and
    then re-adds the extension
    --------------------------------------------------------------

    added drag & drop support

    v1.6 RTM
    --------
    added a group box around the progress bar with changing caption
    text explaining basically what the bar is keeping track of

    v1.5 beta
    ---------
    fixed 'ops.dat' reading code to allow for commented lines starting

    with '//'. this allows for easier management of this file.
    buttons are now disabled when performing a task

    Hidden Text edit box is now read only

    ProgressBar is half-way decent (could still use some better
    progression tho)

    inclusion of ProcessMessages to help the window stay focused on more
    than the ProgressBar when performing a task! (thanks guys :))

    LOTS of code cleanup!

    this build is practically a FINAL version and may be converted to
    FINAL once further testing proves its reliability

    v1.1 beta
    ---------
    now uses an external file 'ops.dat' which contains mask pairs for
    checking!

    created an icon

    v1.0 beta
    ---------
    first gui build and name changed to PESplash

    v0.1 beta
    ---------
    all 3 switches are operable(-e | -r | -c)
    embeds data and saves to "newfile.exe"
    can now retreive embedded data from watermarked file
    returns space available for watermarking

    do NOT try to use this with a packed file, it'll crash
    or at best, it'll make the packed file useless!

    v0.3 alpha
    ----------
    now takes text input for embedding

    converts text to a binary string and saves changes to "testbin.bin"

    v0.2 alpha
    ----------
    got rid of the temp file (now stores text bytes into memory
    directly)

    saves changed CODE section as a binary file "testbin.bin"

    v0.1 alpha
    ----------
    initial build

    uses one set of masks only, no table yet

    creates temp text representation of valid opcodes from CODE section
    of a PE file

    creates temp text representation of changed CODE section with ALL
    bytes found by mask0 or mask1
Seedling http://seedling.dcmembers.com/


Description
Executable code steganography

Features
I have submitted a rather unusual app that takes a different approach in steganography.  I (with the help of friends and Oleh Yuschuk's disassembly engine  ) developed this application way back in 2003-2004. The app is called PESplash.  It embeds text into windows exe files using interchangeable assembly opcodes.

With this app you can create your own 'keys' (ops.dat file) that will be able to embed/read hidden text via a binary stream based on the interchangeable codes you have in your ops.dat file.  So, it embeds this data into the CODE section of your executable file and will run just as originally compiled without error and yet contains hidden data.  Now, be warned, if you decide on interchangeable opcodes and you are wrong, then your application will most likely not run correctly. the default ops.dat file contains most zero flag, interchangeable codes that should not be a problem to swap (but it's not perfect).

So to summarize, it embeds text into your executable files.  This could be used in nefarious ways (and is the reason i never released it to the public).  Use with restraint, but it's a pretty cool way of tracking who is downloading your files (if released in the wild), send messages, etc.

Anyway, that's my submission, enjoy.

Also, please note that this is free and without protection, however, if you plan on using this in a corporate/commercial product, then you must contact me for proper compensation.

Screenshots
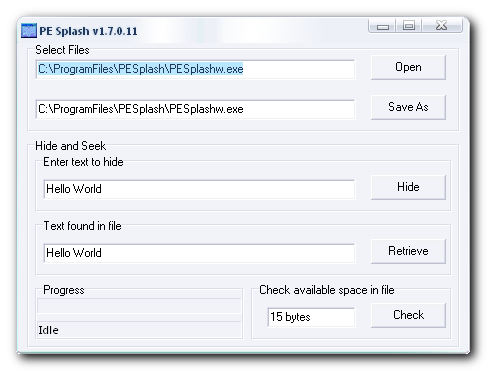
PES_SS.png

Usage
Installation
unzip this to a dir of your choice and run it :)

Using the Application
Select an unpacked app, have it scan for the amount of bytes available (per your ops.dat file keyfile) then write the text to the file, done. to retrieve the embedded text, just open the file and select retrieve, done. :)

Uninstallation
just delete the files that you unzipped, done :)

Known Issues
this will not work with already packed (compressed) executable files. that is, it will seem to work, but the file will not work.

« Last Edit: December 26, 2008, 06:13 AM by seedling »

mouser

  • First Author
  • Administrator
  • Joined in 2005
  • *****
  • Posts: 40,931
    • Gathering Badge
    • Plugin Coding Medal
    • Participated in NANY Challenge Seventeen Times
    • Cody Award
    • Coding Snacks
    • Volunteers/Staff
Re: NANY 2009 Release: PESplash
« Reply #1 on: December 26, 2008, 04:41 AM »
Very cool  :up:

f0dder

  • [Well, THAT escalated quickly!]
  • Charter Honorary Member
  • Joined in 2005
  • ***
  • Posts: 9,153
    • Participated in NANY Challenge Once
Re: NANY 2009 Release: PESplash
« Reply #2 on: December 26, 2008, 11:58 AM »
Wicked :)
- carpe noctem

app103

  • That scary taskbar girl
  • Global Moderator
  • Joined in 2006
  • *****
  • Posts: 5,888
    • Participated in NANY Challenge Six Times
    • Coding Snacks
    • Gathering Badge
    • Cody Award
    • Volunteers/Staff
Re: NANY 2009 Release: PESplash
« Reply #3 on: December 28, 2008, 01:40 PM »
but it's a pretty cool way of tracking who is downloading your files (if released in the wild)

What exactly do you mean by that?

Codebyte

  • "Premature Optimization is the root of all evil."
  • Supporting Member
  • Joined in 2007
  • **
  • Posts: 160
    • Participated in NANY Challenge Once
    • Coding Snacks
    • Plugin Coding Medal
Re: NANY 2009 Release: PESplash
« Reply #4 on: December 28, 2008, 06:30 PM »
Quote
but it's a pretty cool way of tracking who is downloading your files (if released in the wild)
Quote
What exactly do you mean by that?

Im interested as well; what did you mean?
CodeByter.com - http://www.codebyter.com

seedling

  • Charter Member
  • Joined in 2005
  • ***
  • Posts: 129
    • Participated in NANY Challenge Twice
    • Coding Snacks
Re: NANY 2009 Release: PESplash
« Reply #5 on: December 29, 2008, 05:13 AM »
if you tag your exectuable with 'johnny noname 155-345' (if the space allows) and you find it out in 'the wild' without permisssion, then you'll be able to know exactly where the source came from 'i.e. johnny noname 155-345' simple as that. just use the app and see for yourself.

Jibz

  • Cold Warrior
  • Developer
  • Joined in 2005
  • ***
  • Posts: 1,187
    • Programming School - Stage 1 Medal
    • Coding Snacks
    • Participated in NANY Challenge Four Times
Re: NANY 2009 Release: PESplash
« Reply #6 on: December 29, 2008, 08:20 AM »
It sounds like a really neat idea .. is it similar in functionality to hydan?
"A problem, properly stated, is a problem on it's way to being solved" -Buckminster Fuller
"Multithreading is just one damn thing after, before, or simultaneous with another" -Andrei Alexandrescu

seedling

  • Charter Member
  • Joined in 2005
  • ***
  • Posts: 129
    • Participated in NANY Challenge Twice
    • Coding Snacks
Re: NANY 2009 Release: PESplash
« Reply #7 on: December 29, 2008, 09:34 PM »
It sounds like a really neat idea .. is it similar in functionality to hydan?

i never heard of this app, but reading a brief overview of their paper, the idea seems a lot the same (and perhaps even better in some aspects).  one key difference is that mine does not use a 'set' group of interchangable opcodes, but rather, reads them from a user created ops.dat file. which effectively is used as a key to encode/read what you're trying to hide.
« Last Edit: December 29, 2008, 09:35 PM by seedling »

Original address: https://www.donationcoder.com/forum/index.php?topic=16347.0