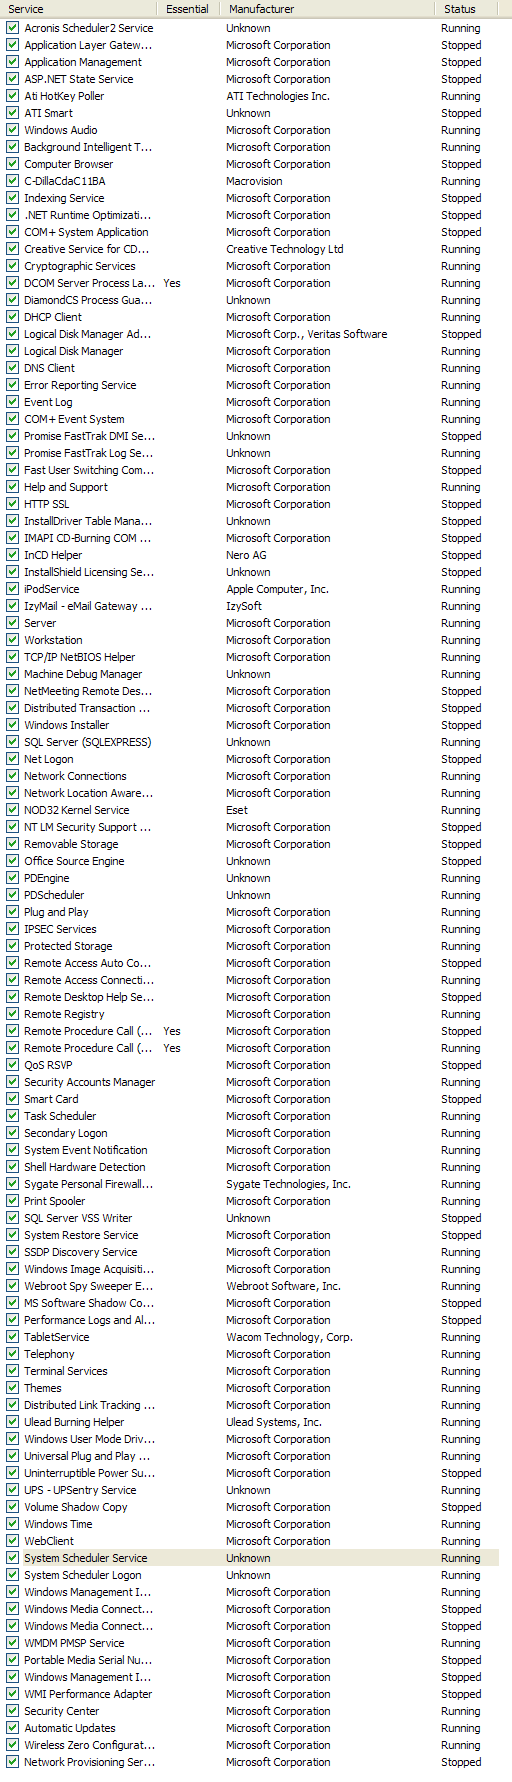
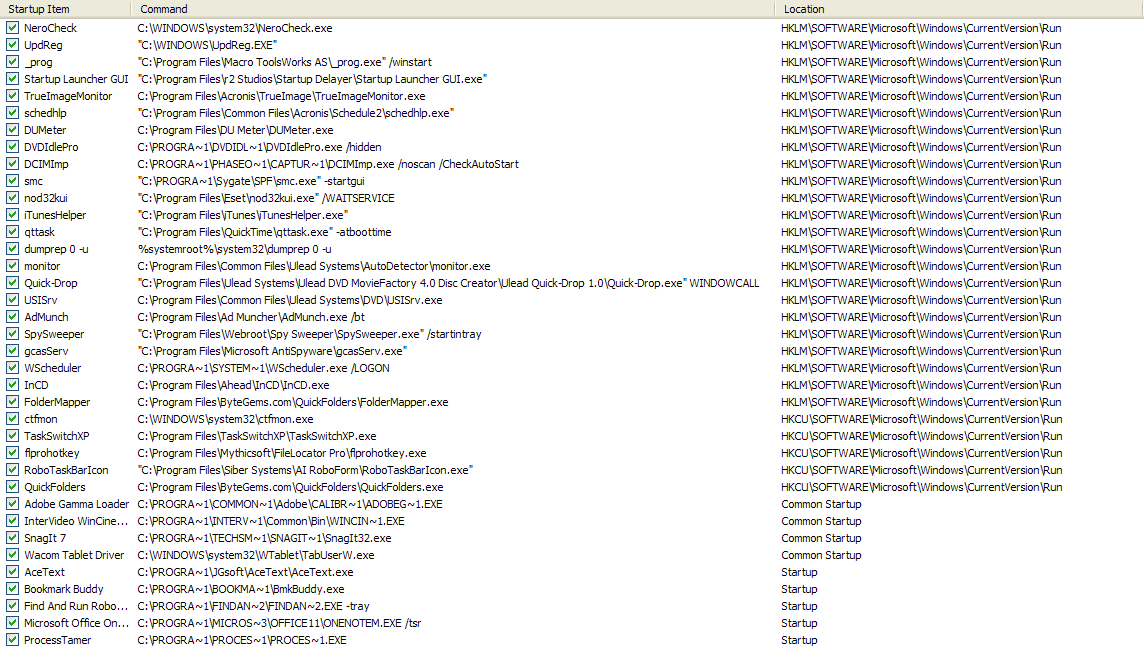
I discovered an unknown service present on my system (not good) and can't find any relevant info on the web.
The service is simply called 'K' and referrs to the file Local Settings\Temp\K.EXE
Unfortunately I had deleted K.EXE by the time I found it so can't send it off for analysis.
I have done websearches on K.EXE but haven't found any references that seem to refer to the same thing (there are some finds but the other parts of their descriptions aren't found on my system).
K.EXE had three associated registry entries (Control Set\Service entries) similar to this:
Anyone else experienced this or can shed light on it.
I have written to ESET (NOD32) support to ask for advice but without the K.EXE file I doubt they can help much.
The service is simply called 'K' and referrs to the file Local Settings\Temp\K.EXE
Unfortunately I had deleted K.EXE by the time I found it so can't send it off for analysis.
I have done websearches on K.EXE but haven't found any references that seem to refer to the same thing (there are some finds but the other parts of their descriptions aren't found on my system).
K.EXE had three associated registry entries (Control Set\Service entries) similar to this:
Code
REGEDIT4

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\K]
"Type"=dword:00000110
"Start"=dword:00000004
"ErrorControl"=dword:00000001
"ImagePath"=hex(2):48,3a,5c,4c,4f,43,41,4c,53,7e,31,5c,54,65,6d,70,5c,4b,2e,65,\
  78,65,00
"DisplayName"="K"
"ObjectName"="LocalSystem"

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\K\Security]
"Security"=hex:01,00,14,80,90,00,00,00,9c,00,00,00,14,00,00,00,30,00,00,00,02,\
  00,1c,00,01,00,00,00,02,80,14,00,ff,01,0f,00,01,01,00,00,00,00,00,01,00,00,\
  00,00,02,00,60,00,04,00,00,00,00,00,14,00,fd,01,02,00,01,01,00,00,00,00,00,\
  05,12,00,00,00,00,00,18,00,ff,01,0f,00,01,02,00,00,00,00,00,05,20,00,00,00,\
  20,02,00,00,00,00,14,00,8d,01,02,00,01,01,00,00,00,00,00,05,0b,00,00,00,00,\
  00,18,00,fd,01,02,00,01,02,00,00,00,00,00,05,20,00,00,00,23,02,00,00,01,01,\
  00,00,00,00,00,05,12,00,00,00,01,01,00,00,00,00,00,05,12,00,00,00

[HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\K\Enum]
"0"="Root\\LEGACY_K\\0000"
"Count"=dword:00000001
"NextInstance"=dword:00000001
Anyone else experienced this or can shed light on it.
I have written to ESET (NOD32) support to ask for advice but without the K.EXE file I doubt they can help much.