


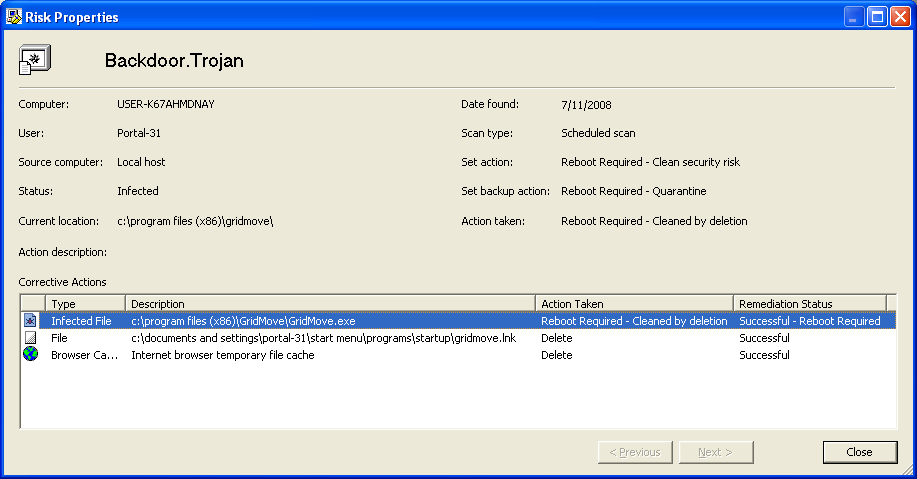
Today (July 11, 2008), Symantec AntiVirus identified GridMove as a Backdoor.Trojan with the 7/9/2008 rev. 3 definition file and deleted GridMove.exe from the Program Files folder and also the application link from Startup.
I imagine I can just re-install GridMove and it should be okay, but I'm pretty sure this is a false positive by Symantec AntiVirus since the previous definition file did not detect an infection, no other programs are infected, and GridMove launches on startup every time. Has anyone else had the same problem? I'm running Windows XP x64 if that makes any difference.
Here's a picture of what Symantec AntiVirus did:
[attach]


 )
 ), without giving me a chance to save it!


 I hope it'll bring some good improvements. Right now, I already have the "drag to edge" method working with multi-monitors, a long-overdue feature.
 )


 luckily for Symantec, GridMove is NOT a virus/malware.


 VanDragt.com

 avast! spotted the false positive again.


