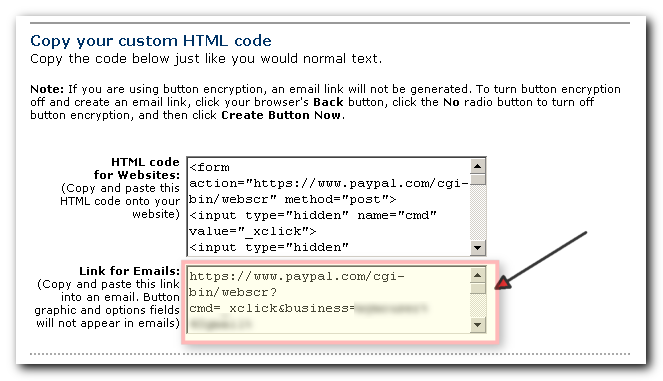
The encrypted PayPal link code is standard HTML format, you could handle the actual HTML tags (to avoid security issues) and just allow people to enter the encrypted part of the code, which is just an encryption of the email address etc.
Here is mine:
<form action="https://www.paypal.com/cgi-bin/webscr" method="post">
<input type="hidden" name="cmd" value="_s-xclick">
<input type="image" src="https://www.paypal.com/en_US/i/btn/x-click-butcc-donate.gif" border="0" name="submit" alt="Make payments with PayPal - it's fast, free and secure!">
<input type="hidden" name="encrypted" value="-----BEGIN PKCS7----- Lots of encryption junk -----END PKCS7-----
">
</form>
As far as I can tell the "Lots of encrypted junk" is just that, not executable code. It is decoded on the PayPal page referred to using the
PKCS7 routines embedded in the PayPal page.
the first three lines are standard (you could supply them so that you know they are OK along with the <form> tags). The only user customisable bit is the image file used for the button. You could choose that as a site default (or even use a DC specific image for the button).
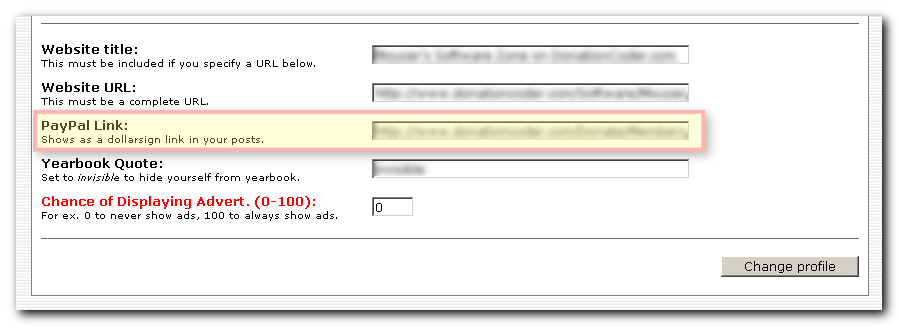
The only user specific info required is the 'Lots of encrypted junk' which could be cut and paste into a user profile field, and automatically used to generate the button script (a trivial PHP script could do that).
If invalid data is supplied PayPal would not be able to decrypt it and generate its own error (and anyway it would not be ina DC page - so no threat to DC). If some one used somebody elses code they would effectively send all their donations to them, but the same thing could happen now if someone copied another users URL from the 'donate' button on the forum pages!!!
Just a thought.




 Online TrID file identifier
 SeqBox