DonationCoder.com forum
 
Read-only archive. This is a static copy of the DonationCoder.com forum. Reading and searching work as before; logging in, posting and private messages do not.
Archive of 2026-10-21 · About this archive · Main site

Author Topic: Can't *think* of a robust password? - free PC Tools Password Utilities  (Read 15,740 times)

Wordzilla

  • Forum Search Daemon
  • Charter Member
  • Joined in 2005
  • ***
  • Posts: 470
    • Programming School - Deluxe Bonus Medal
    • Participated in NANY Challenge Once
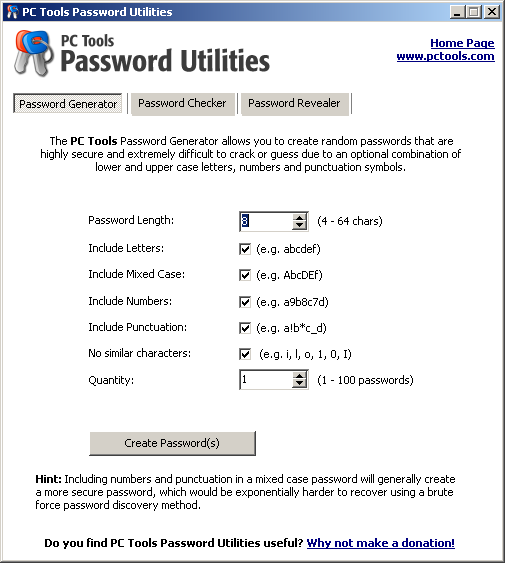
It's basically the desktop version of their popular Secure Password Generator web service. 392KB standalone executable, no installation required, freeware (well actually donationware). In addition to password generation functions, it claims to be able to reveal hidden Internet Explorer passwords (not yet tested here).

[attach=#]
jgpaiva

  • Artificial Idiocy
  • Global Moderator
  • Joined in 2006
  • *****
  • Posts: 4,727
    • Cody Award
    • Participated in NANY Challenge Once
    • Coding Snacks
    • Portugal Inhabitant
    • Linux User
Also don't forget veign's online MakePassword ;)

yksyks

  • Supporting Member
  • Joined in 2006
  • **
  • Posts: 476
How about Gibson's Perfect Passwords?

Dormouse

  • Supporting Member
  • Joined in 2007
  • **
  • Posts: 1,992
I'm not sure I really understand the point of standalone password generators. The password can be relatively hard to guess or crack and can be used - but how is it to be remembered? It will be too random/long for most humans memory to be reliable. And, if it is recorded somewhere, couldn't it be found by someone else?

I understand the point inside a password manager which will only need one master password. I understand the value of the two input system (master password and account name) that effectively only needs one master password and use this myself on minor accounts where security does not really matter (though I still record them in Keepass). But I don't really understand the point of just generating uncrackable impossible to remember passwords without a method of recording them that is itself secure.

PhilB66

  • Supporting Member
  • Joined in 2007
  • **
  • Posts: 1,522
Also check The Password Meter and Hackosis' strong passwords test (PHP open source code available for download).

Lashiec

  • Member
  • Joined in 2006
  • **
  • Posts: 2,374
I'm not sure I really understand the point of standalone password generators. The password can be relatively hard to guess or crack and can be used - but how is it to be remembered? It will be too random/long for most humans memory to be reliable. And, if it is recorded somewhere, couldn't it be found by someone else?

I understand the point inside a password manager which will only need one master password. I understand the value of the two input system (master password and account name) that effectively only needs one master password and use this myself on minor accounts where security does not really matter (though I still record them in Keepass). But I don't really understand the point of just generating uncrackable impossible to remember passwords without a method of recording them that is itself secure.

You can use a notetaker that automatically encrypts its contents, like LockNote or fSekrit or use the "Remember passwords" option in most browsers, it's just another method to achieve the same that KeePass or RoboForm do.

Dormouse

  • Supporting Member
  • Joined in 2007
  • **
  • Posts: 1,992
Yes, I agree it works fine if you use LockNote etc - as you say that would make it another way of achieving a Password Manager system. Longer winded though, unless you are already using Locknote etc.

Don't know about the 'remember password option' in browsers. Certainly convenient, but not sure it is that secure.

Lashiec

  • Member
  • Joined in 2006
  • **
  • Posts: 2,374
Well, it's secure as long as you're the only one using the computer, or witnessing its use by other person, or you protect them with a master password. The file containing the passwords is encrypted with the Triple DES algorithm (in Opera, and I think in Firefox as well), so no problem there.

Don't know about the scheme used by IE, anyway, one of the advantages of storing the passwords in the browser is taking advantage of the portability most browsers offer, and IE is not one of them :)

EDIT: Removed confusing abbreviation (or something)
« Last Edit: March 27, 2008, 01:23 PM by Lashiec »

f0dder

  • [Well, THAT escalated quickly!]
  • Charter Honorary Member
  • Joined in 2005
  • ***
  • Posts: 9,153
    • Participated in NANY Challenge Once
Don't know about the 'remember password option' in browsers. Certainly convenient, but not sure it is that secure.
Firefox can protect the remembered passwords with a master password - I don't know what grade of security it uses, and I personally don't use that feature.
- carpe noctem

Dormouse

  • Supporting Member
  • Joined in 2007
  • **
  • Posts: 1,992
Yes, I suppose that with a master password the browsers are probably secure enough. And convenient so long as you only use that browser (much less convenient otherwise).

Original address: https://www.donationcoder.com/forum/index.php?topic=12811.0