Hi all.
I recently stumbled across some rather disturbing information recently; it seems Microsoft has taken it upon themselves to insert personally identifiable information into every executable linked with their link.exe. This information is refered to as the "rich signature", and is located between the DOS stub and PE header (example below). Apparently thus far they've used it as evidence against several high-profile virus writers.
Thus far the only information i have found on this signature is information on how to prevent it being created by link.exe, and a passing reference to it on the archived SysInternals forums. Out of sheer morbid curiosity, I'd like to ask if anyone else has any further information on the rich signature. If your information is available from an objectionable location, please PM me about it, otherwise feel free to add it to this thread.
Thanks, Ehtyar.
[attach]
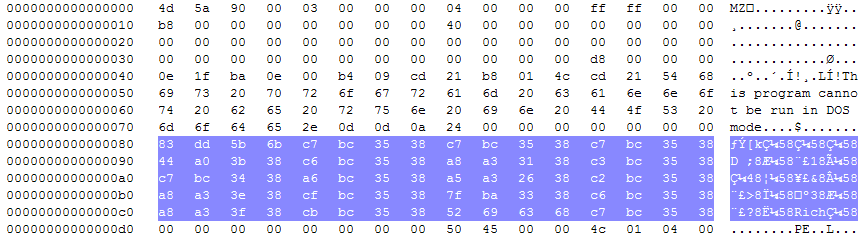


 ), one of the members iirc reverse-engineered link.exe enough to prevent generation of the information.
 - carpe noctem

 RichSignature.txt