


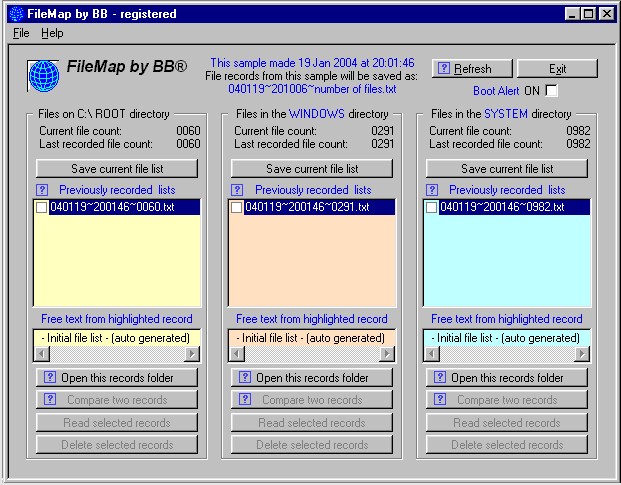
I know that this is fairly trivial - boring even - but let me explain the purpose. With a list of files on the hard drive, you can discover RootKits. First, run the lister under your normal boot O/S. Then boot to a C/D or key drive and run it again. RootKits stealth their files so that they are not seen by normal scans by AV programs, but that means that they do not show up on a normal file list. But, if the same list is created using an O/S that is not infected from a CD or key drive, the files will be on that list. Ideally, the list would be in the form Drive:\Directory\\FileName.Ext and the list would be saved as a text file. In a perfect world, the utility would have the ability to compare the lists and generate a difference list. I seem to have picked up a fairly mean rootkit somewhere - it has crashed IceSword and prevented the new Comodo Firewall from completely installing. I have also had trouble running Sysinternals' Autoruns, so I will have to do this in a fairly elementary fashion.
IDEA: File lister
« on: November 02, 2007, 05:46 AM »






 - carpe noctem